
Welcome!

Unlock your personalized experience.
Sign Up
Tag

Extended detection and response Articles, Guides & Tutorials

3 posts

What Is XDR? How It Compares With EDR, NDR and SIEM

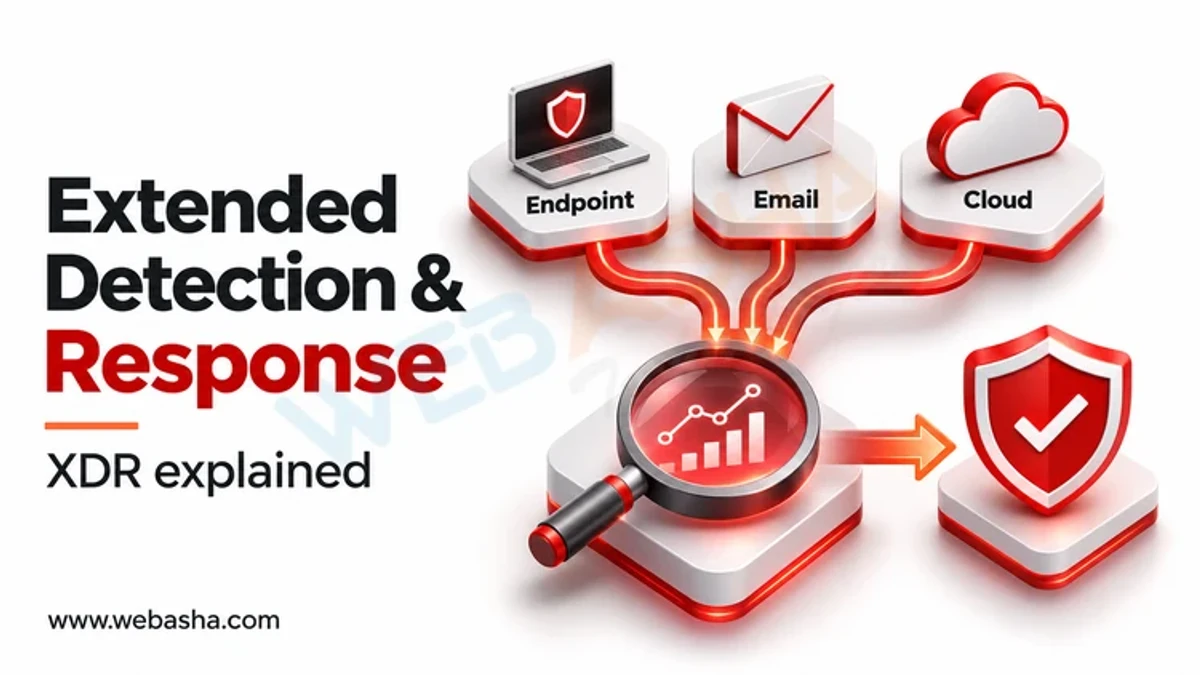
XDR, or extended detection and response, is a security platform that collects telemetry from endpoints, network, email, identity and cloud, correlates it into incidents, and lets analysts respond from one console. EDR covers only endpoints, NDR only network traffic, and a SIEM collects and stores logs from everything but needs more tuning to turn them into incidents.

What Is XDR? How It Compares With EDR, NDR and SIEM

XDR, or extended detection and response, is a security platform that collects telemetry from endpoints, network, email, identity and cloud, correlates it into incidents, and lets analysts respond from one console. EDR covers only endpoints, NDR only network traffic, and a SIEM collects and stores logs from everything but needs more tuning to turn them into incidents.

MDR and XDR for DevOps Teams: How They Work and When You Need Them

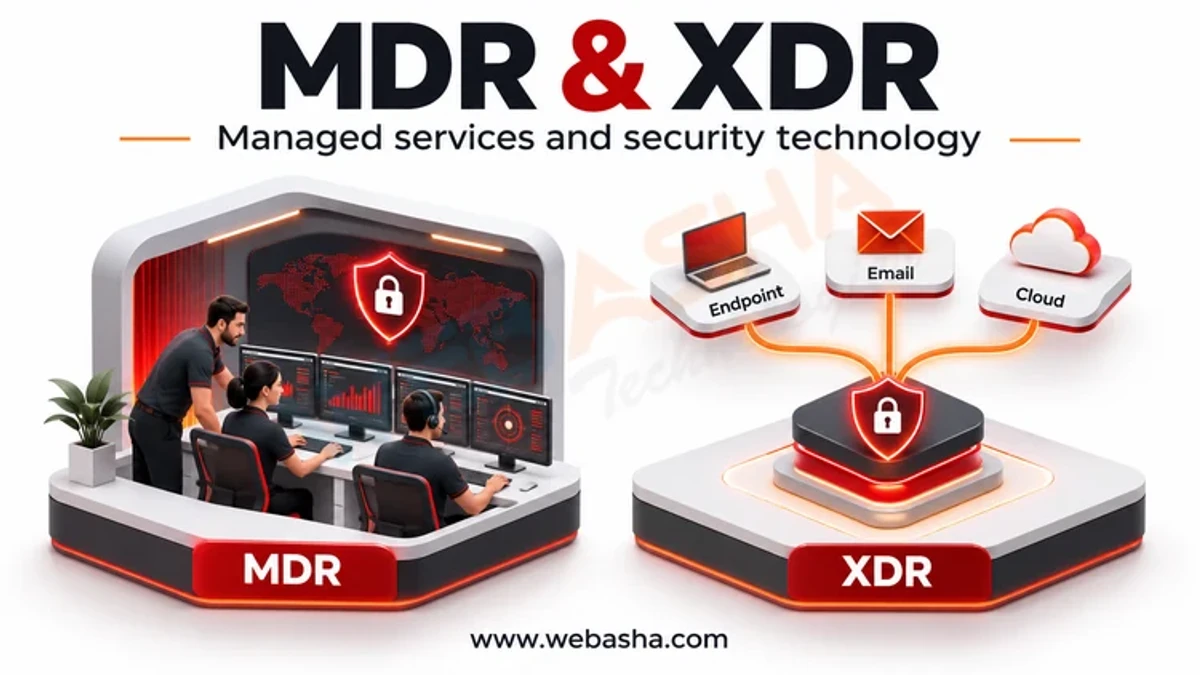
XDR (extended detection and response) is a technology platform that collects and correlates security data from endpoints, cloud, identity, email and network to detect and respond to attacks. MDR (managed detection and response) is a service: a provider's analysts monitor your environment around the clock, investigate alerts and take or guide response actions, often using an XDR platform.







