MDR and XDR for DevOps Teams: How They Work and When You Need Them
XDR (extended detection and response) is a technology platform that collects and correlates security data from endpoints, cloud, identity, email and network to detect and respond to attacks. MDR (managed detection and response) is a service: a provider's analysts monitor your environment around the clock, investigate alerts and take or guide response actions, often using an XDR platform.
Topic: SOC & Blue Team in Cybersecurity & Ethical Hacking · Explainer
Also covers: DevOps & Platform Engineering
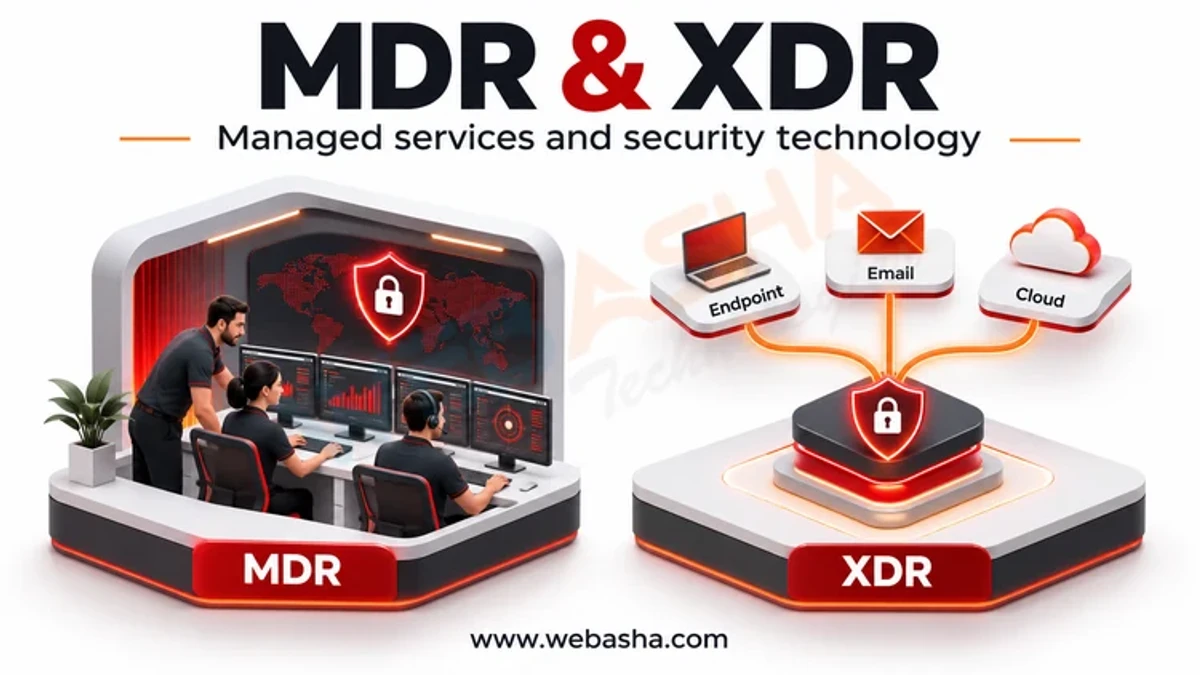
Quick answer: XDR (extended detection and response) is a technology platform that collects and correlates security data from endpoints, cloud, identity, email and network to detect and respond to attacks. MDR (managed detection and response) is a service: a provider's analysts monitor your environment around the clock, investigate alerts and take or guide response actions, often using an XDR platform. For DevOps teams, the question is whether either covers what you actually run: cloud control planes, Kubernetes, CI/CD systems and containers, not just laptops. Many small and mid-sized teams choose MDR because they cannot staff a 24x7 security operations centre.
Key takeaways
- XDR is something you buy and operate; MDR is people who operate detection for you.
- Coverage of cloud audit logs, Kubernetes and CI/CD is the main gap in many offerings.
- Agree in writing which response actions the provider may take without asking.
- Your own logging quality limits what any MDR or XDR can detect.
- Keep incident response ownership in-house even when monitoring is outsourced.
Table of Contents
- What Is the Difference Between MDR and XDR?
- Why Do DevOps Environments Need Different Coverage?
- Which Telemetry Must You Provide?
- How Does Runtime Detection Work in Kubernetes?
- How Do You Choose Between MDR, XDR or Both?
- What Should You Ask an MDR Provider?
- How Do You Onboard Successfully?
- References
What Is the Difference Between MDR and XDR?
| XDR | MDR | |
|---|---|---|
| What it is | Detection and response platform | Managed service with analysts |
| Who watches alerts | Your team | Provider's SOC, 24x7 |
| Response | Tools you trigger, some automated | Provider acts or advises within agreed limits |
| Best for | Teams with security analysts | Teams without round-the-clock security staff |
| Main risk | Alerts nobody reviews | Provider lacks context about your systems |
For the technology itself, see our antivirus vs EDR vs XDR comparison.
Why Do DevOps Environments Need Different Coverage?
Traditional detection focuses on Windows laptops and servers. DevOps estates add attack paths that endpoint agents do not see: stolen cloud access keys used through APIs, malicious changes to CI/CD pipelines, exposed Kubernetes dashboards, compromised container images and secrets leaked in repositories. The MITRE ATT&CK cloud matrix and containers matrix list these techniques. An MDR or XDR offering that cannot ingest cloud and cluster telemetry will miss them.
Which Telemetry Must You Provide?
| Source | Examples | Detects |
|---|---|---|
| Cloud control plane | AWS CloudTrail, Azure Activity Log, Google Cloud Audit Logs | Key misuse, privilege changes, data exfiltration |
| Cloud threat detection | GuardDuty, Defender for Cloud, Security Command Center | Known malicious behaviour |
| Identity | Entra ID, Okta, IAM Identity Center sign-in logs | Account takeover |
| Kubernetes | API server audit logs, runtime sensors | Privileged pods, exec into containers |
| CI/CD and code | GitHub or GitLab audit logs, pipeline logs | Pipeline tampering, token abuse |
| Hosts and containers | EDR agents, Falco | Malware, crypto miners, reverse shells |
CISA's event logging guidance lists priority log sources and retention.
How Does Runtime Detection Work in Kubernetes?
Runtime sensors watch system calls inside nodes and containers. Falco, a CNCF project, ships rules such as alerting when a shell starts in a container:
helm repo add falcosecurity https://falcosecurity.github.io/charts
helm install falco falcosecurity/falco -n falco --create-namespace

# test: open a shell in a pod, then check Falco's output
kubectl exec -it deploy/web -- sh -c "id"
kubectl logs -n falco -l app.kubernetes.io/name=falco | grep -i "shell"
Forward these alerts to your XDR or MDR provider so they can correlate them with cloud and identity events.
How Do You Choose Between MDR, XDR or Both?
- No security analysts: MDR, ideally with cloud and Kubernetes coverage.
- Small security team, business hours: XDR plus MDR for nights and weekends.
- Mature SOC: XDR or SIEM run in-house, with specialist retainers for major incidents.
What Should You Ask an MDR Provider?
- Which cloud, Kubernetes and CI/CD log sources do you ingest natively?
- What response actions can you take, and which need our approval?
- How quickly do you notify us of a confirmed critical incident, and how?
- Can you support reporting obligations, such as CERT-In's six-hour rule in India?
- Who owns the data, where is it stored, and how long is it kept?
- How do you tune detections to reduce false positives from deployments?
How Do You Onboard Successfully?
- Inventory accounts, clusters and pipelines, and enable audit logging everywhere.
- Share architecture diagrams and normal deployment patterns so deployments are not flagged as attacks.
- Agree an escalation list and test it with a simulated alert.
- Align with your incident response plan, following NIST SP 800-61 Rev. 3.
- Review monthly: missed detections, false positives and coverage gaps.
Related: DevOps security best practices. WebAsha offers SOC analyst training.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.