NIST Cybersecurity Framework: Functions, Profiles and How to Apply It
The NIST Cybersecurity Framework (CSF) is a voluntary, risk-based guide for managing cybersecurity. Version 2.0, released by NIST on 26 February 2024, organises outcomes into six Functions: Govern, Identify, Protect, Detect, Respond and Recover.
Topic: Cybersecurity Foundations in Cybersecurity & Ethical Hacking · Explainer
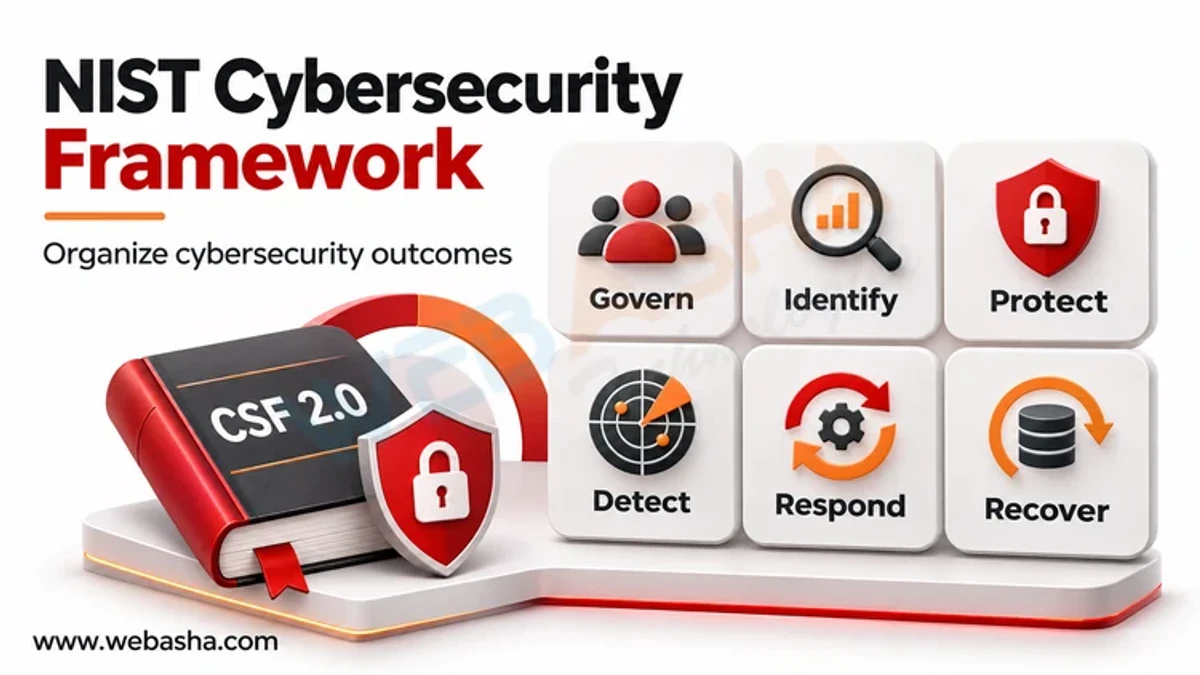
Quick answer: The NIST Cybersecurity Framework (CSF) is a voluntary, risk-based guide for managing cybersecurity. Version 2.0, released by NIST on 26 February 2024, organises outcomes into six Functions: Govern, Identify, Protect, Detect, Respond and Recover. To apply it, you build a Current Profile describing which outcomes you achieve today, define a Target Profile based on your risks and obligations, then close the gaps with a prioritised action plan. Tiers 1 to 4 describe how rigorous your risk management practices are. CSF does not prescribe tools; it links to standards such as ISO/IEC 27001 and the CIS Controls for detail.
Key takeaways
- CSF 2.0 applies to any organisation, not just critical infrastructure.
- Govern is the new sixth Function and covers strategy, roles, policy and supply chain risk.
- Profiles turn the framework into a gap analysis for your organisation.
- Tiers measure maturity of risk management, not a score to maximise.
- Informative references map CSF outcomes to detailed controls.
Table of Contents
- What Changed in CSF 2.0?
- How Is the CSF Core Structured?
- What Are Organizational Profiles?
- What Do the Tiers Mean?
- How Do You Implement CSF Step by Step?
- How Does CSF Fit with ISO 27001 and Indian Rules?
- What Mistakes Should You Avoid?
- References
What Changed in CSF 2.0?
NIST released CSF 2.0 on 26 February 2024, the first major update since version 1.1 in 2018. It widened the scope to all organisations, added the Govern Function, and added Quick Start Guides, implementation examples and an online reference tool. The full text is NIST CSWP 29.
How Is the CSF Core Structured?
The Core is a hierarchy: Functions contain Categories, which contain Subcategories (specific outcomes).
| Function | ID | Focus |
|---|---|---|
| Govern | GV | Strategy, roles, policy, oversight, supply chain risk |
| Identify | ID | Assets, risk assessment, improvement |
| Protect | PR | Identity and access, awareness, data and platform security |
| Detect | DE | Continuous monitoring, analysis of adverse events |
| Respond | RS | Incident management, analysis, reporting, mitigation |
| Recover | RC | Restoring assets and operations, communication |
What Are Organizational Profiles?
A Current Profile records which CSF outcomes you achieve now and how well. A Target Profile records the outcomes you need, given your risk appetite, legal duties and business goals. The difference is your gap. NIST also supports Community Profiles, shared targets for a sector or technology, which you can adopt as a starting point.
What Do the Tiers Mean?
| Tier | Name | Typical sign |
|---|---|---|
| 1 | Partial | Ad hoc, reactive security |
| 2 | Risk Informed | Risk is understood but not organisation-wide policy |
| 3 | Repeatable | Approved policies applied consistently |
| 4 | Adaptive | Practices improve continuously from lessons and threat data |
Tiers guide your target; not every organisation needs Tier 4.
How Do You Implement CSF Step by Step?
- Set scope: whole organisation, a business unit or one system.
- Gather inputs: risk assessments, laws, contracts, existing policies.
- Build the Current Profile by assessing each relevant Subcategory.
- Define the Target Profile and target Tier with leadership.
- Analyse gaps and rank them by risk and cost.
- Create an action plan with owners and dates, using the Quick Start Guides.
- Implement, measure and repeat the cycle at least yearly.
How Does CSF Fit with ISO 27001 and Indian Rules?
CSF outcomes map to controls in ISO/IEC 27001:2022 and the CIS Controls; the CSF reference tool lists these informative references. CSF is not mandatory in India, but it helps organise duties such as the CERT-In Directions: 6-hour incident reporting fits Respond (RS), and 180-day log retention supports Detect (DE).
What Mistakes Should You Avoid?
- Treating CSF as a checklist instead of a risk-based conversation.
- Skipping Govern, so no one owns decisions or budget.
- Aiming for Tier 4 everywhere regardless of risk.
- Writing profiles once and never updating them.
New to the framework? Start with the NIST CSF for beginners, then read about zero trust security. WebAsha offers governance, risk and compliance training.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.