
Welcome!

Unlock your personalized experience.
Sign Up
Tag

Broken access control Articles, Guides & Tutorials

3 posts

Broken Access Control Explained: How IDOR Bugs Are Found and Fixed

Broken access control means an application lets a user do something their role or ownership should not allow, such as reading another customer's order, calling an admin API as a normal user, or changing a price field. It was ranked first in the OWASP Top 10 2021. IDOR (insecure direct object reference) is the best-known form: the app trusts an ID in the request instead of checking ownership.
What Is IDOR? Insecure Direct Object Reference Explained With Examples

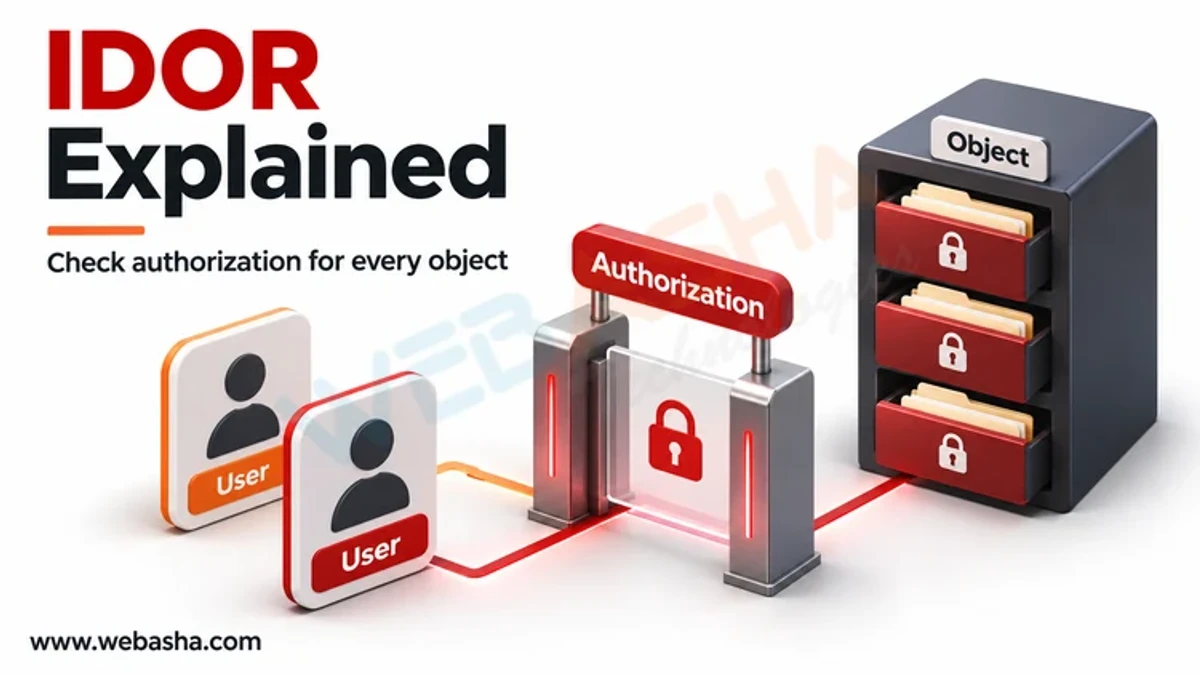
An Insecure Direct Object Reference (IDOR) is an access control flaw. An application uses an identifier supplied by the user, such as an order number or file ID, to fetch a record, but never checks that the logged-in user is allowed to see or change that record. Changing the identifier can then expose another customer's data.









