
Welcome!

Unlock your personalized experience.
Sign Up
Tag

Prompt injection Articles, Guides & Tutorials

3 posts

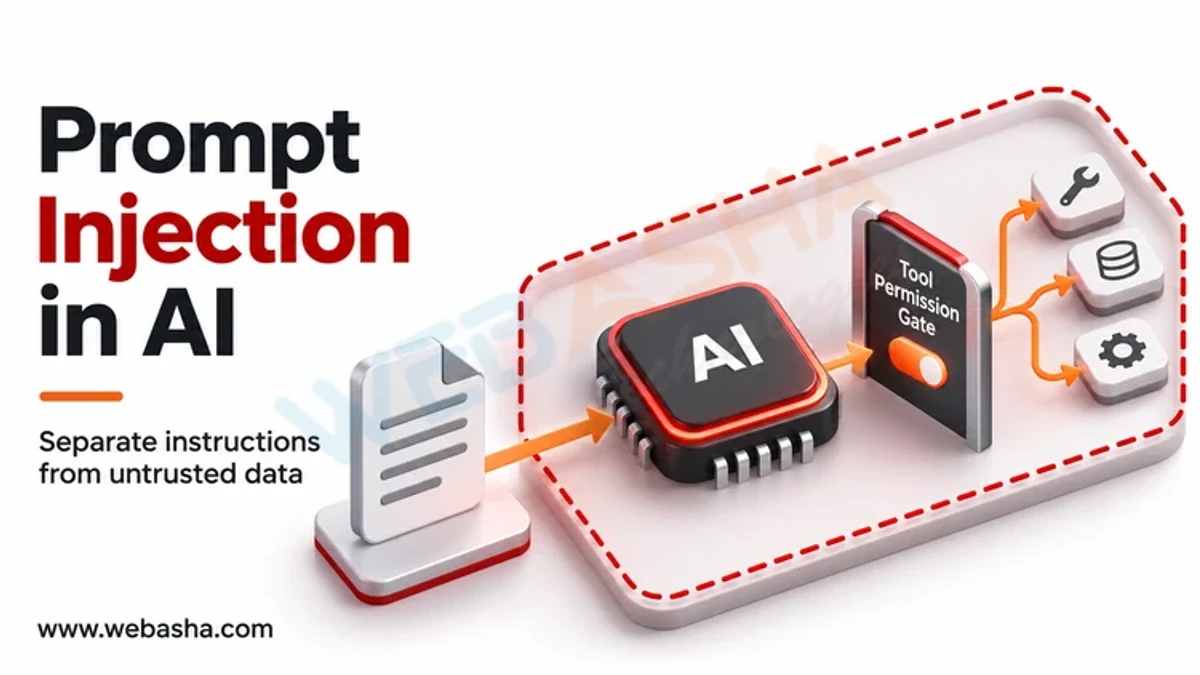
Prompt Injection in Generative AI: How It Works and How to Defend

Prompt injection is an attack in which text supplied to a large language model (LLM) makes it ignore its intended instructions and follow the attacker's instead. In direct injection, a user types the malicious instructions. In indirect injection, the instructions are hidden in content the AI reads, such as a web page, email, document or code comment, so the user may never see them.
AI vs Cybersecurity: How Defenders Adapt to AI-Powered Attacks

AI helps attackers write better phishing, clone voices, research targets and adjust code faster, so defenders must adapt controls rather than buy a single AI product. The most effective changes are phishing-resistant MFA, out-of-band verification for payments, faster patching of internet-facing systems, behaviour-based detection and staff training on deepfakes.

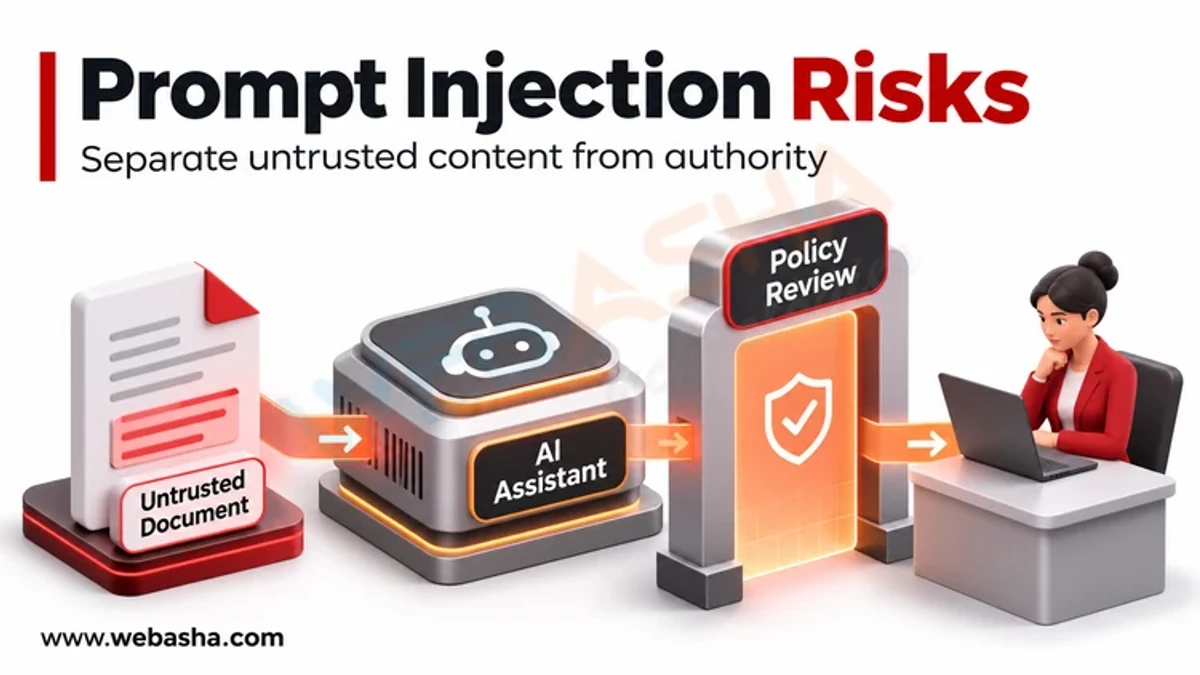
When an AI Assistant Turns Against You: Prompt Injection Privacy Risks

An AI assistant can be turned against you through prompt injection: hidden instructions inside an email, web page, calendar invite or document that the assistant reads and then follows as if you had asked. OWASP ranks prompt injection first (LLM01) in its 2025 Top 10 for LLM applications. The privacy risk grows with access.









