Best Open-Source SIEM Tools: Wazuh, Security Onion and More
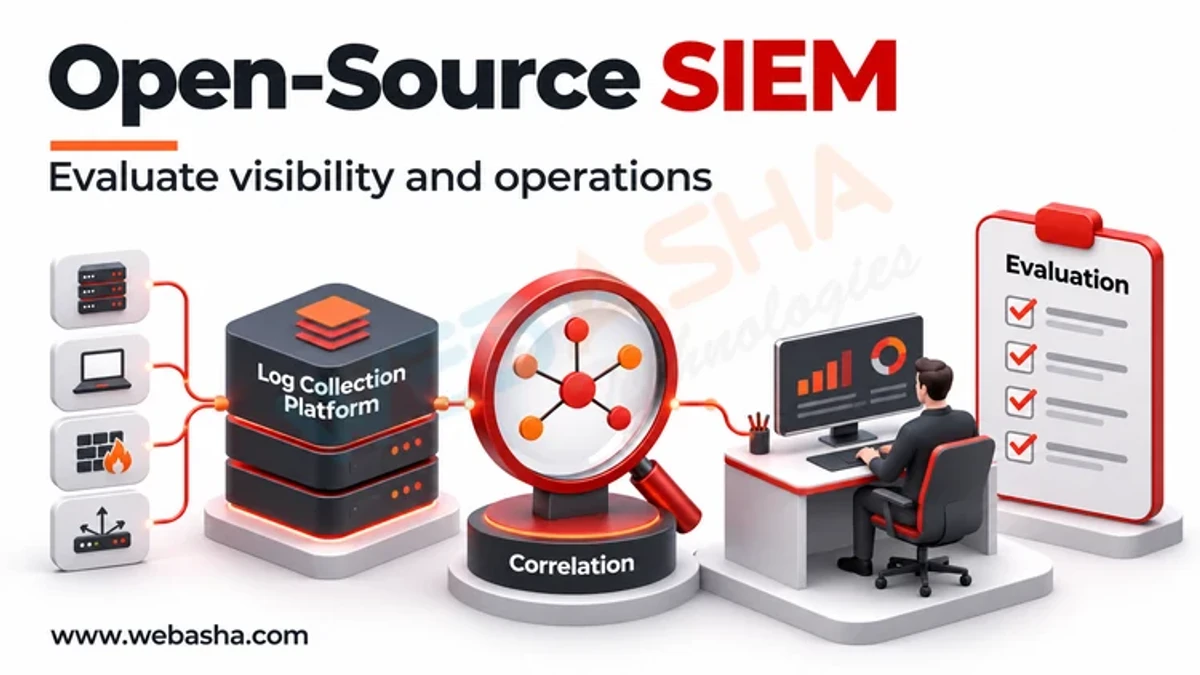
The main free and open-source SIEM options are Wazuh for host-based detection and compliance, Security Onion for network security monitoring and threat hunting, and OpenSearch with its Security Analytics plugin for log analytics with detection rules. Elastic and Graylog offer free editions under source-available or dual licences, so check their terms.
Topic: SOC & Blue Team in Cybersecurity & Ethical Hacking · Tools
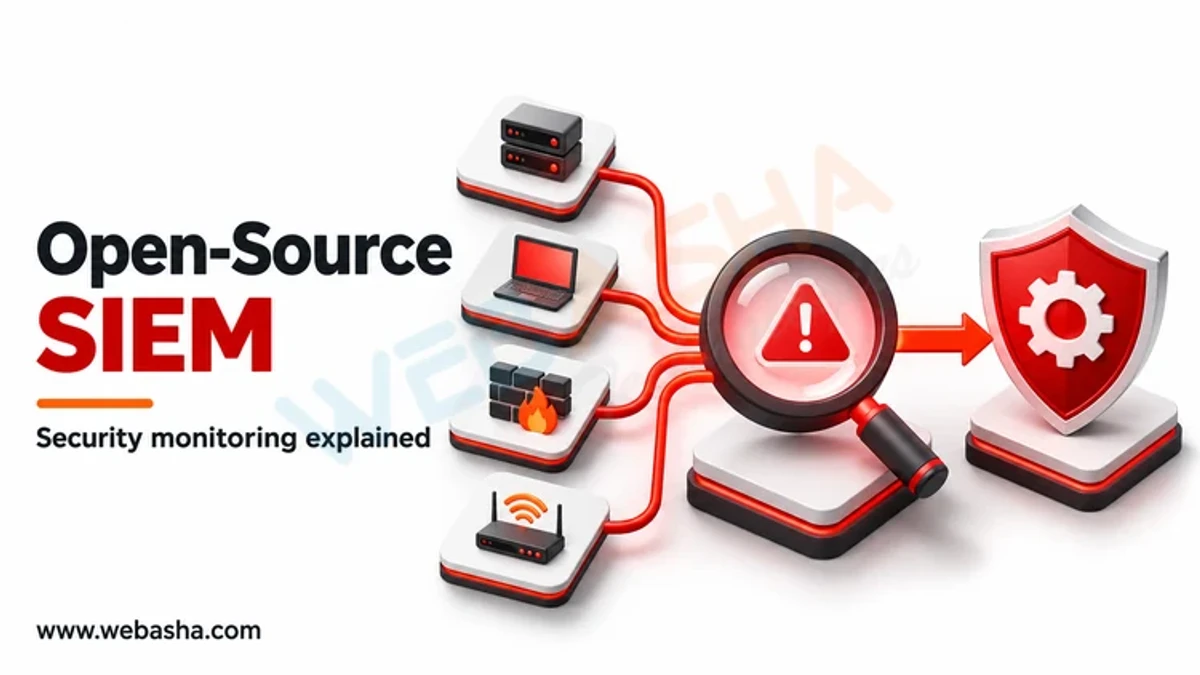
Quick answer: The main free and open-source SIEM options are Wazuh for host-based detection and compliance, Security Onion for network security monitoring and threat hunting, and OpenSearch with its Security Analytics plugin for log analytics with detection rules. Elastic and Graylog offer free editions under source-available or dual licences, so check their terms. AlienVault OSSIM, often listed in older articles, has been retired by LevelBlue. Choose by your log sources, team skills and hardware, and budget for the time to tune rules.
Key takeaways
- Wazuh is the most complete open-source option for endpoint-centred SIEM.
- Security Onion bundles network monitoring, hunting and case management.
- OSSIM is retired; do not start new deployments on it.
- Free does not mean cheap: storage, tuning and staff time dominate cost.
- Check licences: Graylog Open uses SSPL, Elastic offers AGPL among others.
Table of Contents
- How Do the Main Options Compare?
- How Does Wazuh Work?
- What Does a Custom Detection Rule Look Like?
- How Do You Choose?
- How Can You Learn SIEM Skills Free?
- Which Log Sources Should You Onboard First?
- How Do Sigma Rules Make Detections Portable?
- How Much Storage Will You Need?
- References
How Do the Main Options Compare?
| Tool | Strength | Licence | Best for |
|---|---|---|---|
| Wazuh | Agents, file integrity, vulnerability detection, compliance mapping | GPLv2 | Small to mid-size teams protecting servers and endpoints |
| Security Onion | Network monitoring, Suricata and Zeek, hunting, cases | Free and open platform, with Elastic components | Network-focused SOCs and training labs |
| OpenSearch Security Analytics | Scalable search with Sigma-based detectors | Apache 2.0 | Teams already running OpenSearch |
| Elastic Security | Detection rules, timelines, large rule library | AGPL, SSPL or Elastic Licence; some features paid | Teams comfortable with Elastic |
| Graylog Open | Easy log management and dashboards | SSPL (source-available) | Log centralisation before full SIEM |
| Splunk Free | Learning Splunk search language | Proprietary, 500 MB per day | Study, not production |
OSSIM: LevelBlue, formerly AT&T Cybersecurity and AlienVault, announced in December 2024 that OSSIM is retired.
How Does Wazuh Work?
Agents on endpoints send logs and inventory to a Wazuh server, which decodes them and applies rules; alerts are stored in an indexer and viewed in a dashboard. A single-host lab install:
curl -sO https://packages.wazuh.com/4.x/wazuh-install.sh
sudo bash ./wazuh-install.sh -a        # all-in-one: indexer, server, dashboard
# then install an agent on a Linux host, pointing at the manager
sudo WAZUH_MANAGER="10.0.0.5" dnf install -y wazuh-agent
sudo systemctl enable --now wazuh-agent
Check the current version path in the Wazuh quickstart before installing.
What Does a Custom Detection Rule Look Like?
This Wazuh rule raises severity when one source fails SSH logins many times, building on built-in rule 5716 (SSH authentication failure):
<!-- /var/ossec/etc/rules/local_rules.xml -->
<group name="local,sshd,">
  <rule id="100100" level="10" frequency="8" timeframe="120">
    <if_matched_sid>5716</if_matched_sid>
    <same_source_ip />
    <description>Possible SSH brute force: 8 failures in 2 minutes from one IP</description>
    <mitre><id>T1110</id></mitre>
  </rule>
</group>
sudo /var/ossec/bin/wazuh-logtest # paste a sample log line to test
sudo systemctl restart wazuh-managerHow Do You Choose?
- List your log sources: endpoints, firewalls, cloud, network sensors.
- Estimate daily log volume and retention; size storage accordingly.
- Match the tool to your team's skills and time for tuning.
- Confirm the licence suits your use, especially if you offer it as a service.
- Pilot with real logs for a month before committing.
How Can You Learn SIEM Skills Free?
Build a lab with Wazuh and one Windows and one Linux agent, generate attacks from a Kali VM, and write rules that detect them. Our guides on what SIEM is and SOC analyst skills help, or talk to a WebAsha training advisor about SOC training.
Which Log Sources Should You Onboard First?
Start with sources that show logins, new processes and admin changes. On Windows, these Security and System event IDs, documented by Microsoft, catch many common attacks:
| Event ID | Meaning | Why it matters |
|---|---|---|
| 4624 / 4625 | Successful / failed logon | Brute force, unusual logon types and hours |
| 4688 | New process created | Malicious commands, with command-line auditing on |
| 4720 | User account created | Attacker persistence |
| 4728 / 4732 | Member added to a security group | Privilege escalation |
| 7045 | New service installed | Remote execution tools and persistence |
| 1102 | Security log cleared | Covering tracks |
On Linux, start with authentication logs (/var/log/secure or auth.log), auditd and sudo. Then add firewall, VPN, DNS and cloud audit logs such as AWS CloudTrail.
# Linux: watch changes to sudoers with auditd
sudo auditctl -w /etc/sudoers -p wa -k sudoers_change
sudo ausearch -k sudoers_change --start today
How Do Sigma Rules Make Detections Portable?
Sigma is an open, YAML-based format for detection rules. One rule can be converted into queries for different SIEMs with the sigma-cli tool and the right backend plugin, so switching platforms does not mean rewriting everything.
pip install sigma-cli
sigma plugin install elasticsearch
# convert a Windows rule to a Lucene query using the ECS field mapping
sigma convert -t lucene -p ecs_windows my_rules/shadow_copy_deletion.yml
OpenSearch Security Analytics and Elastic both ship many Sigma-derived rules. Review each rule's false-positive notes before enabling it.
How Much Storage Will You Need?
Estimate from events per second (EPS), average event size and retention. This calculation is a planning aid; measure your real EPS during a pilot.
def siem_storage_gb(eps, avg_bytes=500, days=90, replicas=1, compression=0.5):
    daily_gb = eps * avg_bytes * 86400 / 1024**3
    return round(daily_gb * days * (1 + replicas) * compression, 1)

for eps in (100, 500, 2000):
    print(eps, "EPS ->", siem_storage_gb(eps), "GB for 90 days")
At 500 EPS, 500-byte events and 90 days with one replica, that comes to roughly 1,800 GB before index overhead. Retention rules matter too: CERT-In's 2022 directions require 180 days of logs for covered entities in India.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.