What are the best Wireshark filters for OT cybersecurity monitoring and threat detection?
Wireshark display filters narrow OT captures by protocol, such as Modbus, DNP3 or Profinet, by device discovery and by suspicious behaviour like unexpected hosts or write commands. Capture passively, using a SPAN port or network TAP, and never actively scan fragile control systems. These filters help defenders map devices, audit protocols and spot abnormal traffic early.
Topic: Security Tools, Authorized Labs & CTFs in Cybersecurity & Ethical Hacking · Explainer
Also covers: SOC & Blue Team
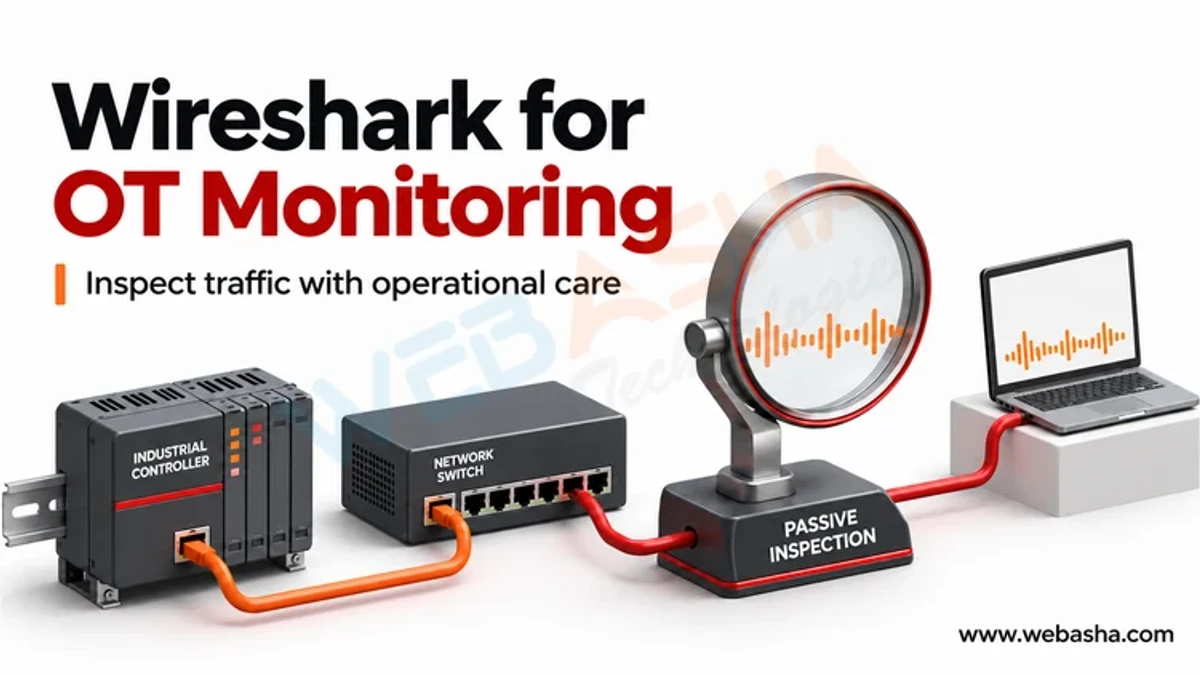
Quick answer: Wireshark display filters narrow OT captures by protocol, such as Modbus, DNP3 or Profinet, by device discovery and by suspicious behaviour like unexpected hosts or write commands. Capture passively, using a SPAN port or network TAP, and never actively scan fragile control systems. These filters help defenders map devices, audit protocols and spot abnormal traffic early.
Key takeaways
- Use modbus, dnp3 or s7comm as display filters to isolate industrial traffic.
- Flag Modbus write function codes from unknown hosts, since writes change process state.
- Capture on a mirror port, never inline, in a live plant.
Table of Contents
- What Is Wireshark and Why Is It For OT Networks?
- Network Discovery Filters
- Suspicious Activity Filters
- General Utility Filters for OT Engineers
- Modbus Protocol Filters
- Filters for Other OT/ICS Protocols
- Why Use These Filters for Cybersecurity?
- Best Practices for Using Wireshark in OT Environments
- Conclusion
In Operational Technology (OT), security is critical. From manufacturing plants to power grids, OT environments rely on specific industrial protocols like Modbus, DNP3, and Profinet to operate safely. But with growing cyber threats, network visibility has become more important than ever.
Wireshark, a free and open-source network protocol analyzer, offers powerful tools to monitor, analyze, and secure OT traffic. This post shows how to use Wireshark effectively for OT cybersecurity using practical filters and examples.
What Is Wireshark and Why Is It For OT Networks?
Wireshark allows cybersecurity professionals to capture and analyze packets from OT network traffic. In industrial networks, it helps detect suspicious activities, troubleshoot communication issues, and audit protocol behavior in real-time.
OT environments often use non-IT protocols, so using Wireshark with OT-specific filters is essential to identify:
-
Broadcast storms
-
Unauthorized devices
-
Protocol misuse
-
Malicious commands (e.g., writing Modbus registers)
Network Discovery Filters
Wireshark filters help identify devices and communication patterns in the network. Use these filters to discover unknown or unauthorized endpoints:
| Use Case | Wireshark Filter |
|---|---|
| Find broadcast traffic | eth.dst == ff:ff:ff:ff:ff:ff |
| ARP responses (IP to MAC mapping) | arp.opcode == 2 |
| DHCP Discover/Request | bootp.option.type == 53 |
| Unique MAC addresses | !(eth.addr in {00:00:00:00:00:00}) |
| Unique IPs in a range | ip.addr >= 192.168.0.0 and ip.addr <= 192.168.255.255 |
Suspicious Activity Filters
Use these filters to detect malicious behavior such as scanning, tunneling, or malformed packets in OT networks:
| Activity | Wireshark Filter |
|---|---|
| Port scanning | tcp.flags.syn == 1 && tcp.flags.ack == 0 |
| Uncommon ports | `tcp.dstport < 11 |
| High order ports | tcp.dstport > 1024 |
| Modbus over non-standard ports | modbus && tcp.port!= 502 |
| Malformed packets | `tcp.analysis.flags && (tcp.len == 0 |
| Long TCP sessions for tunneling | tcp.analysis.bytes_in_flight > 10000 |
| OT devices communicating with Internet | !(ip.dst >= 10.0.0.0 && ip.dst <= 10.255.255.255) &&!(ip.dst >= 172.16.0.0 && ip.dst <= 172.31.255.255) &&!(ip.dst >= 192.168.0.0 && ip.dst <= 192.168.255.255) |
General Utility Filters for OT Engineers
These filters help you isolate traffic by IP, MAC, stream, or port, especially useful during incident response or traffic audits:
| Use Case | Wireshark Filter |
|---|---|
| Follow Modbus stream | tcp.stream eq |
| Filter by IP | ip.addr == |
| Filter by MAC address | eth.addr == |
| Conversations by port | tcp.port == |
Modbus Protocol Filters
Modbus is one of the most commonly used protocols in industrial control systems. Use these filters to track Modbus activity:
| Filter Purpose | Wireshark Filter |
|---|---|
| Show Modbus traffic | modbus |
| TCP port 502 traffic | tcp.port == 502 |
| Write single coil | modbus.func_code == 5 |
| Write multiple registers | modbus.func_code == 16 |
| Device identification | modbus.func_code == 43 |
Filters for Other OT/ICS Protocols
OT networks may use a range of protocols depending on the vendor. Here are key filters:
| Protocol | Wireshark Filter |
|---|---|
| S7 (Siemens) | tcp.port == 102 / s7comm |
| DNP3 | tcp.port == 20000 / dnp3 |
| EtherNet/IP | tcp.port == 44818 / enip |
| Profinet | eth.type == 0x8892 |
| BACnet/IP | udp.port == 47808 / bacnet |
Why Use These Filters for Cybersecurity?
Cyberattacks on industrial environments often mimic normal behavior. With Wireshark filters, you can:
-
Detect command injections
-
Identify unauthorized engineering stations
-
Spot traffic going to the public internet
-
Audit device configurations
-
Visualize attack patterns using packet coloring and follow streams
Best Practices for Using Wireshark in OT Environments
| Practice | Tip |
|---|---|
| Capture traffic during normal operations | Helps set a performance baseline |
| Use display filters for specific protocols | Avoids overload from irrelevant data |
| Label known devices and IPs | Easier to spot anomalies |
| Store PCAP files securely | Packet captures may contain sensitive ICS commands |
| Integrate with IDS tools | Use Wireshark in combination with Suricata or Snort for deeper analysis |
Conclusion
Wireshark is a powerful asset for OT cybersecurity professionals. Whether you’re tracking Modbus write operations or spotting unusual TCP sessions, using the right filters can mean the difference between a secure system and a compromised one.
With these ready-to-use display filters, you’ll be better equipped to monitor, investigate, and respond to threats in industrial control environments.
To take this further with guided labs and an instructor, see our hands-on network defence labs.
Related reading
- Understanding Net-Tools | The Essential Network Management Package for Linux
- What are the most important Wireshark filters every cybersecurity professional should learn?
- Mastering Wireshark Filters | The Ultimate 2026 Guide for Cybersecurity Professionals, SOC Analysts & Ethical Hackers
Reference
For the authoritative details, see Wireshark documentation.
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.