Cyberattacks at Each OSI Layer and How to Defend Against Them
Attacks can target every layer of the OSI model.
Topic: Cyber Threats, Scams & Online Safety in Cybersecurity & Ethical Hacking · Explainer
Also covers: Cybersecurity Foundations
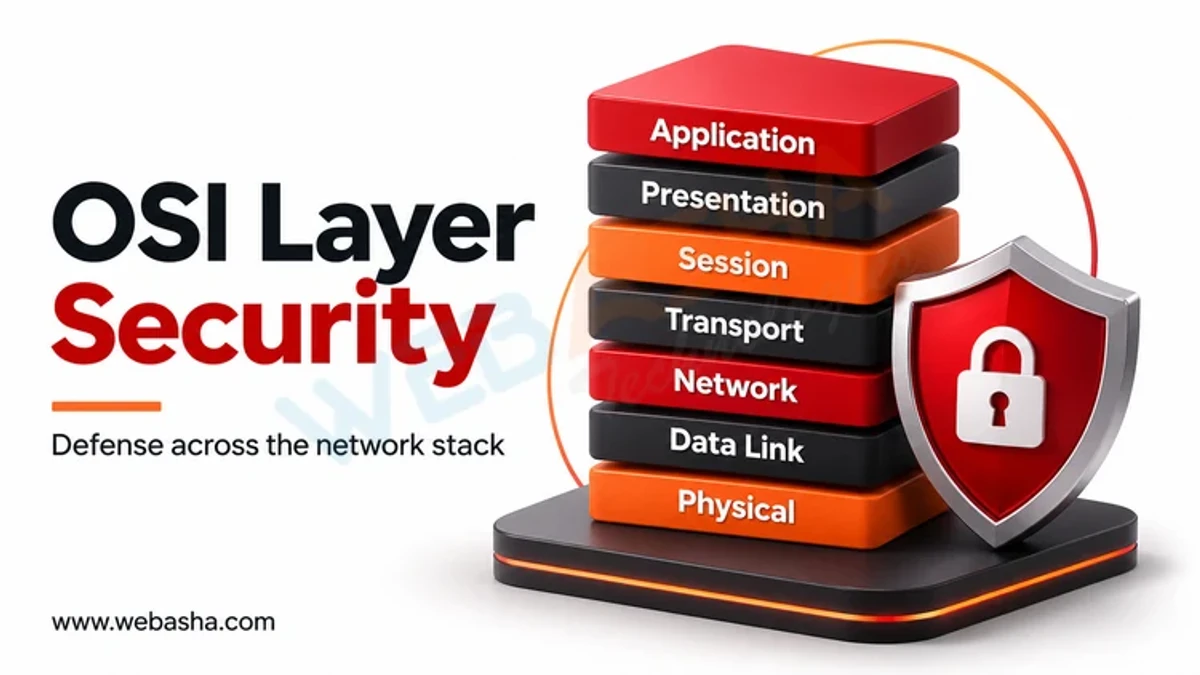
Quick answer: Attacks can target every layer of the OSI model. At the physical layer, attackers tamper with cables or jam Wi-Fi; at the data link layer, they use MAC flooding, ARP spoofing and VLAN hopping; at the network layer, IP spoofing and routing attacks; at the transport layer, SYN floods and port scans; at the session layer, session hijacking; at the presentation layer, TLS downgrade and certificate attacks; and at the application layer, SQL injection, cross-site scripting, DNS attacks and phishing. Defences are layered too: physical security, switch protections, filtering and anti-spoofing, DDoS mitigation, secure session handling, strong TLS and secure coding.
Key takeaways
- Lower-layer attacks often enable higher-layer ones, such as ARP spoofing leading to credential theft.
- Switch features (port security, DHCP snooping, Dynamic ARP Inspection) stop many layer 2 attacks.
- TLS with certificate validation protects against interception at higher layers.
- Most breaches exploit layer 7: applications and people.
- The OSI model is a teaching tool; real protocols do not map perfectly.
Table of Contents
- What Attacks Target Each Layer?
- How Do You Defend Layers 1 and 2?
- How Do You Defend Layers 3 and 4?
- How Do You Defend Layers 5 and 6?
- How Do You Defend Layer 7?
- How Can You Practise Safely?
- References
What Attacks Target Each Layer?
| Layer | Example attacks | Defences |
|---|---|---|
| 7 Application | SQL injection, XSS, DNS spoofing, phishing | Secure coding, WAF, DNSSEC, MFA |
| 6 Presentation | TLS downgrade, weak ciphers, fake certificates | TLS 1.2/1.3 only, HSTS, certificate validation |
| 5 Session | Session hijacking, fixation | Secure cookies, session rotation, timeouts |
| 4 Transport | SYN floods, port scanning | SYN cookies, rate limiting, firewalls |
| 3 Network | IP spoofing, ICMP floods, route hijacking | Ingress filtering, ACLs, RPKI |
| 2 Data link | MAC flooding, ARP spoofing, VLAN hopping, rogue DHCP | Port security, DAI, DHCP snooping, 802.1X |
| 1 Physical | Cable tapping, device theft, Wi-Fi jamming | Physical security, locked racks, monitoring |
The OSI model is defined in ISO/IEC 7498-1; techniques are catalogued in MITRE ATT&CK.
How Do You Defend Layers 1 and 2?
Lock network closets and disable unused switch ports. On managed switches, enable protections against MAC flooding, rogue DHCP servers and ARP spoofing:
! Cisco IOS example
interface range GigabitEthernet1/0/1 - 24
 switchport mode access
 switchport port-security
 switchport port-security maximum 2
 switchport nonegotiate              ! prevents DTP-based VLAN hopping
!
ip dhcp snooping
ip dhcp snooping vlan 10
ip arp inspection vlan 10
interface GigabitEthernet1/0/48
 ip dhcp snooping trust
 ip arp inspection trust
See Cisco's Dynamic ARP Inspection guide. 802.1X ensures only authenticated devices connect.
How Do You Defend Layers 3 and 4?
- Apply ingress and egress filtering to block spoofed source addresses.
- Use RPKI to protect BGP route announcements.
- Enable SYN cookies on servers (
net.ipv4.tcp_syncookies=1on Linux). - Use DDoS protection services for public services, per CISA's DDoS guidance.
- Close unneeded ports and monitor scans.
How Do You Defend Layers 5 and 6?
- Set cookies with
Secure,HttpOnlyandSameSite; rotate session IDs after login. - Allow only TLS 1.2 and 1.3 (RFC 8446) with strong ciphers.
- Enable HSTS (RFC 6797) to prevent downgrade to HTTP.
- Never disable certificate validation in apps or scripts.
# Check which TLS versions a server accepts
nmap --script ssl-enum-ciphers -p 443 example.com
How Do You Defend Layer 7?
Most real breaches happen here. Follow the OWASP Top 10: parameterised queries, output encoding, server-side authorization, and input validation. Use DNSSEC (RFC 4033) and trusted resolvers, phishing-resistant MFA and user training. See common network and application attacks.
How Can You Practise Safely?
Build an isolated lab with virtual machines or GNS3/EVE-NG, practise attacks such as ARP spoofing on your own lab network only, and confirm that switch protections block them. WebAsha's CCNA and ethical hacking courses include such labs. Related: how computer networks work.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.