What Happens Behind the Scenes of a Single Sign-On (SSO) Login?
When you click "Sign in with your company account", the application redirects your browser to an identity provider (IdP) such as Microsoft Entra ID, Okta or Google. The IdP checks whether you already have a session; if not, it asks for your password and MFA. It then sends your browser back to the application with a one-time authorisation code (OpenID Connect) or a signed assertion (SAML).
Topic: Active Directory & Identity Security in Cybersecurity & Ethical Hacking · Explainer
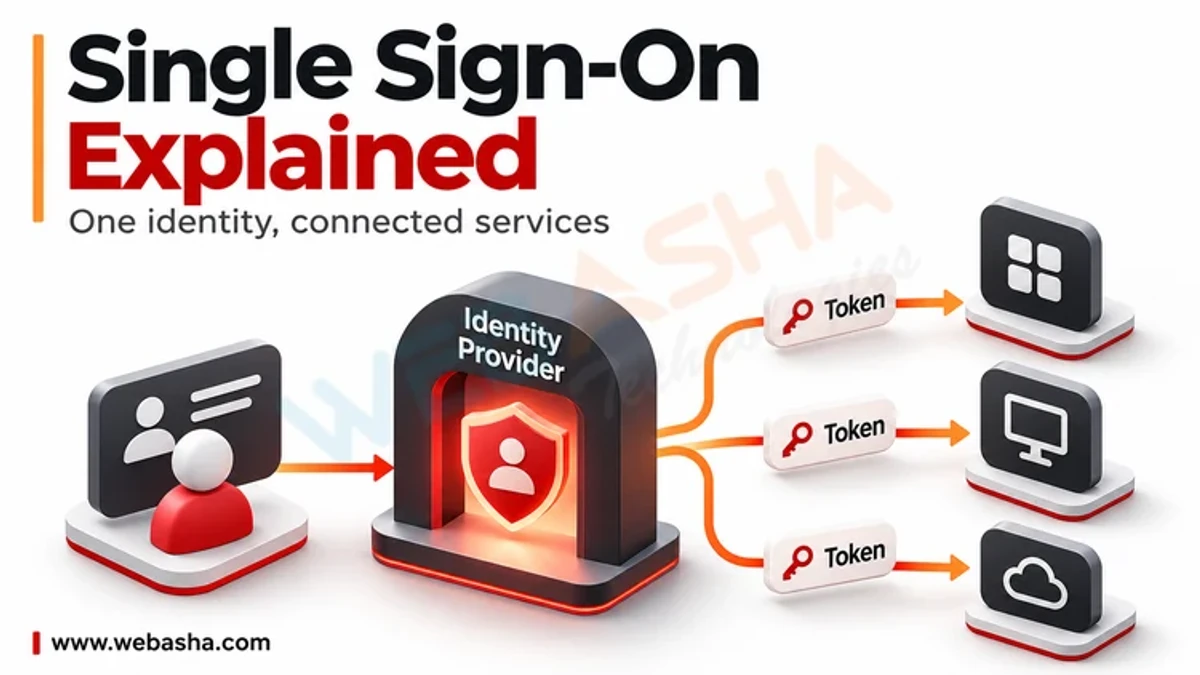
Quick answer: When you click "Sign in with your company account", the application redirects your browser to an identity provider (IdP) such as Microsoft Entra ID, Okta or Google. The IdP checks whether you already have a session; if not, it asks for your password and MFA. It then sends your browser back to the application with a one-time authorisation code (OpenID Connect) or a signed assertion (SAML). The application exchanges the code for an ID token, verifies the signature, issuer, audience, expiry and nonce, and creates its own session. Because the IdP remembers you, the next application signs you in without asking again.
Key takeaways
- The application never sees your password; only the IdP does.
- OpenID Connect uses tokens (JSON); SAML uses signed XML assertions.
- PKCE and state or nonce values stop interception and replay.
- Applications must validate tokens fully, not just decode them.
- One strong login protects many apps, but a compromised IdP session affects all of them.
Table of Contents
- Who Is Involved in an SSO Login?
- What Happens Step by Step With OpenID Connect?
- What Is Inside an ID Token?
- How Is SAML Different?
- How Do Sessions and Logout Work?
- What Are Common SSO Security Mistakes?
- References
Who Is Involved in an SSO Login?
| Role | OIDC name | SAML name |
|---|---|---|
| You and your browser | User agent | User agent |
| The app you want | Relying party (client) | Service provider |
| The login service | OpenID provider | Identity provider |
What Happens Step by Step With OpenID Connect?
- You open the app. It creates random
state,nonceand a PKCE code verifier (RFC 7636), and redirects your browser to the IdP's authorise endpoint. - The IdP checks for an existing session cookie. If none, it shows its own login page, then MFA.
- The IdP may apply conditional access: device compliance, location, risk.
- The IdP redirects back to the app's registered redirect URI with a short-lived
codeand the samestate. - The app checks
state, then calls the IdP's token endpoint server to server with the code and PKCE verifier. - The IdP returns an ID token, and usually an access token and refresh token.
- The app validates the ID token and creates its own session cookie for you.
GET https://login.example-idp.com/authorize?
  response_type=code
  &client_id=crm-app
  &redirect_uri=https://crm.example.com/callback
  &scope=openid%20profile%20email
  &state=af0ifjsldkj
  &nonce=n-0S6_WzA2Mj
  &code_challenge=E9Melhoa2OwvFrEMTJguCHaoeK1t8URWbuGJSstw-cM
  &code_challenge_method=S256
This is the authorisation code flow defined in OpenID Connect Core, with PKCE as RFC 9700 recommends for all clients.
What Is Inside an ID Token?
An ID token is a signed JWT. Decoded, its payload looks like this:
{
  "iss": "https://login.example-idp.com",
  "aud": "crm-app",
  "sub": "248289761001",
  "email": "[email protected]",
  "nonce": "n-0S6_WzA2Mj",
  "iat": 1763100000,
  "exp": 1763103600,
  "amr": ["pwd", "mfa"]
}| Check | Why |
|---|---|
| Signature with the IdP's published key | Proves the IdP issued it |
iss matches the expected IdP | Stops tokens from other issuers |
aud equals your client ID | Stops tokens meant for another app |
exp in the future | Rejects expired tokens |
nonce matches what you sent | Prevents replay |
How Is SAML Different?
With SAML 2.0, the service provider sends an AuthnRequest, and the IdP returns a signed XML Response, usually posted by the browser to the app's Assertion Consumer Service URL. The app validates the XML signature, issuer, audience restriction, time conditions and that the assertion has not been used before. SAML is common for older enterprise apps; OIDC is preferred for new web and mobile apps. Microsoft documents both for Entra ID.
How Do Sessions and Logout Work?
There are at least two sessions: one at the IdP and one in each app. Signing out of one app does not end the IdP session unless the app calls the IdP's logout endpoint, and other apps keep their own sessions until they expire or receive a logout notification. NIST SP 800-63C covers assertion lifetimes and reauthentication in federated systems.
What Are Common SSO Security Mistakes?
- Decoding tokens without verifying the signature.
- Accepting tokens with the wrong audience or issuer.
- Wildcard or loosely matched redirect URIs.
- Skipping
statechecks, allowing login CSRF. - Keeping local password login as a backdoor after SSO is enabled.
- Long-lived sessions with no reauthentication for sensitive actions.
Related: OAuth 2.0 and OpenID Connect and 2FA bypass through OAuth misconfiguration. WebAsha offers identity and access management training.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.