
Welcome!

Unlock your personalized experience.
Sign Up
Tag

Single Sign-On Articles, Guides & Tutorials

2 posts

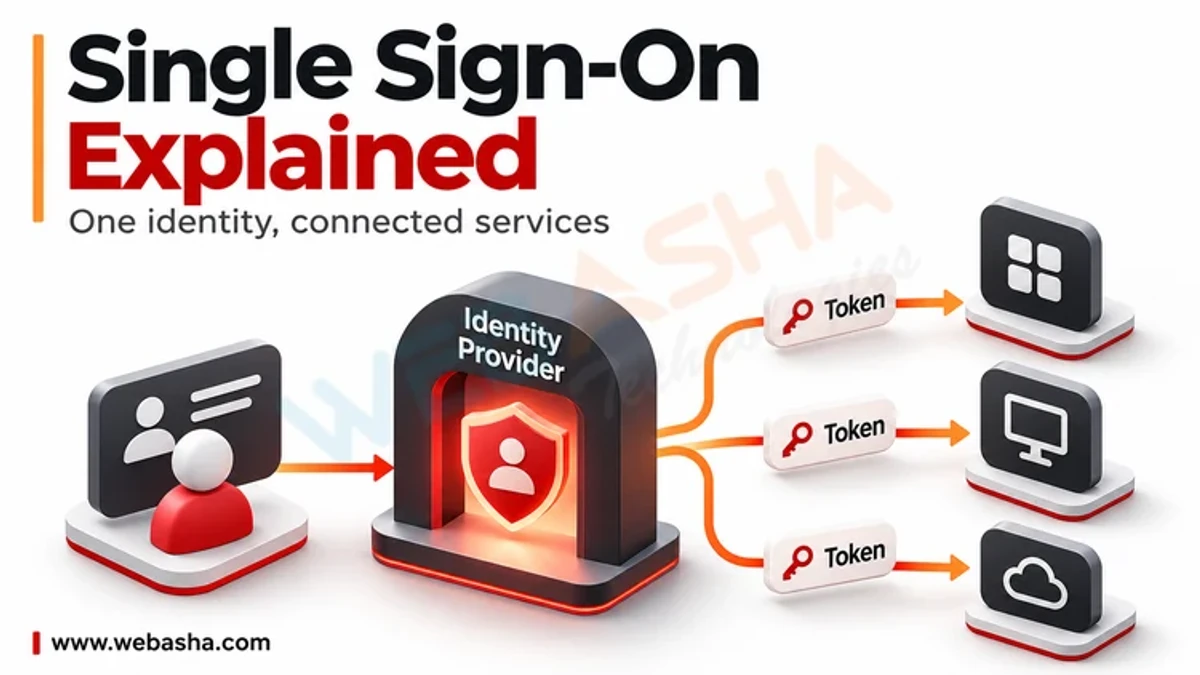
What Happens Behind the Scenes of a Single Sign-On (SSO) Login?

When you click "Sign in with your company account", the application redirects your browser to an identity provider (IdP) such as Microsoft Entra ID, Okta or Google. The IdP checks whether you already have a session; if not, it asks for your password and MFA. It then sends your browser back to the application with a one-time authorisation code (OpenID Connect) or a signed assertion (SAML).
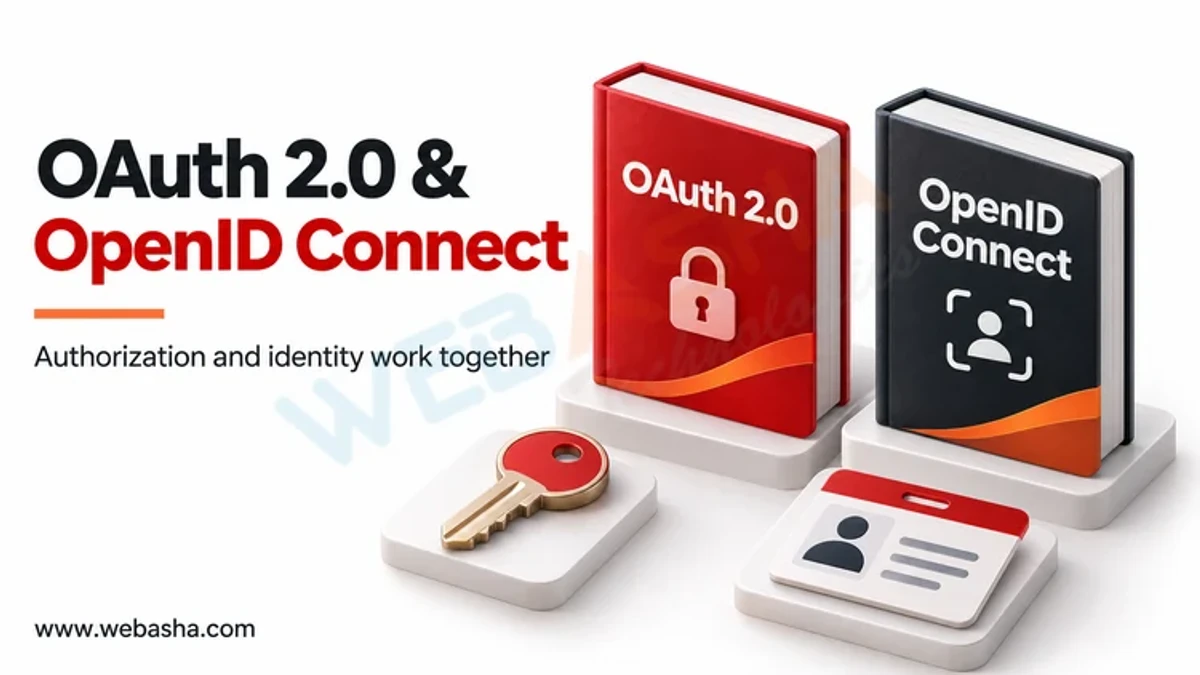

OAuth 2.0 and OpenID Connect: A Simple Guide to Secure Login

OAuth 2.0 is an authorization framework (RFC 6749) that lets an app get limited access to your data on another service without seeing your password, using short-lived access tokens. OpenID Connect (OIDC) is an identity layer built on top of OAuth 2.0 that adds authentication: it returns a signed ID token telling the app who you are. In short, OAuth answers what this app may do, and OIDC answers who this user is.








