What Is hping3? Packet Crafting Explained for Defenders
hping3 is a free, command-line packet crafting tool for Linux and Unix. Instead of sending normal traffic, it lets a user build TCP, UDP, ICMP or raw IP packets with chosen flags, sizes and rates. Security engineers use it in labs to test whether firewall rules and intrusion detection systems behave as expected. Attackers misuse the same ability for stealthy scans and SYN floods.
Topic: Network Security in Cybersecurity & Ethical Hacking · Troubleshooting
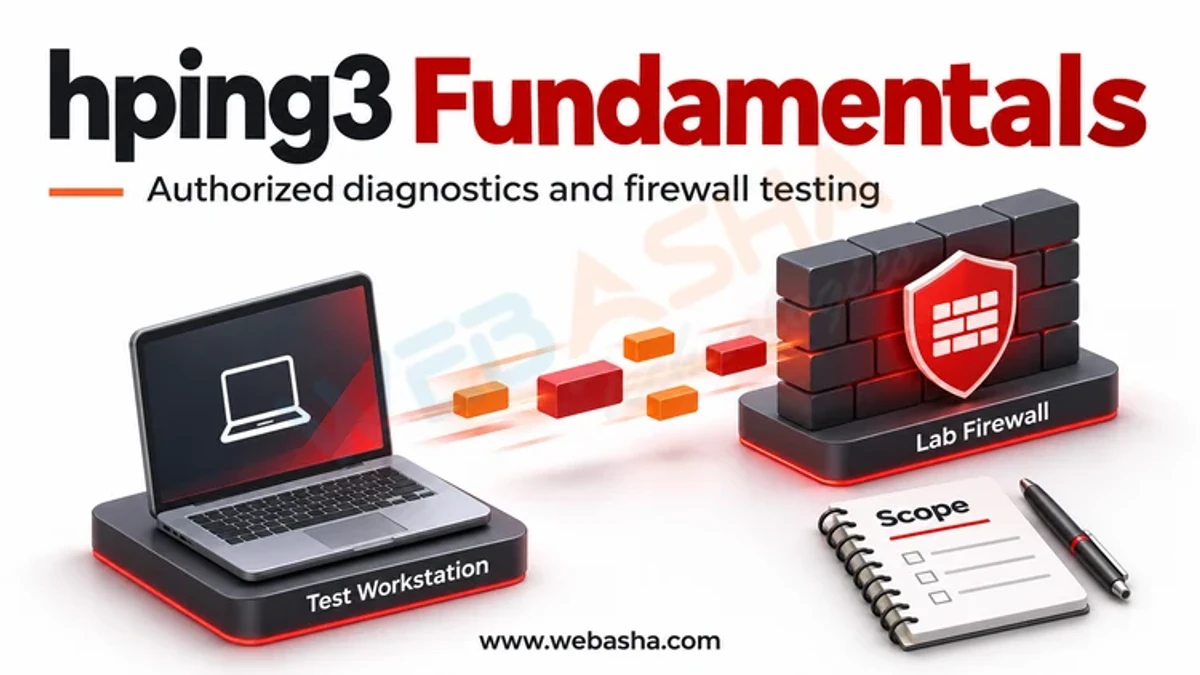
Quick answer: hping3 is a free, command-line packet crafting tool for Linux and Unix. Instead of sending normal traffic, it lets a user build TCP, UDP, ICMP or raw IP packets with chosen flags, sizes and rates. Security engineers use it in labs to test whether firewall rules and intrusion detection systems behave as expected. Attackers misuse the same ability for stealthy scans and SYN floods. Using it against systems you do not own without written permission is illegal under the IT Act 2000. Defenders should watch for unusual flag combinations and floods, and protect services with SYN cookies, rate limiting, stateful firewalls and upstream DDoS protection.
Key takeaways
- hping3 crafts packets by hand; it is a test instrument, not an exploit.
- Its legitimate value is checking that firewalls and IDS rules do what you think.
- Its misuse is mainly denial of service and evasive scanning.
- Crafted traffic often looks abnormal, which helps detection.
- SYN cookies and rate limits blunt the most common abuse.
Table of Contents
- What Is hping3 and What Is Packet Crafting?
- Why Do Engineers and Attackers Use hping3?
- What Are the Legal Rules?
- What Traces Does Crafted Traffic Leave?
- How Do You Detect hping3-Style Traffic?
- How Do You Check SYN Flood Protection on Your Linux Server?
- How Do You Reduce the Impact of Packet Floods?
- References
What Is hping3 and What Is Packet Crafting?
The hping project describes the tool as a TCP/IP packet assembler and analyser. Ordinary programs let the operating system decide how packets look. Packet crafting tools give that control to the user: which TCP flags are set, which source port is used, how large the payload is and how fast packets are sent. The TCP rules they play with are defined in RFC 9293.
Why Do Engineers and Attackers Use hping3?
| Legitimate lab use | Misuse to defend against |
|---|---|
| Verify a firewall drops packets with odd flag combinations | Scans with unusual flags to slip past simple filters |
| Check that an IDS rule fires on a known pattern | Spoofed source scans that hide the real origin |
| Measure path behaviour and MTU issues | SYN floods that exhaust connection tables (T1498) |
| Teach how TCP handshakes work | Service discovery on unauthorised targets (T1046) |
Authorised firewall testing is described in NIST SP 800-115 as part of security testing, and it should be done in a lab or an agreed maintenance window.
What Are the Legal Rules?
Sending crafted or flooding traffic to systems you do not own can disrupt services and amounts to damage or denial of access under Section 43 of the IT Act, 2000, with criminal liability under Section 66. Even a short test against a production site without written approval can cause outages. Keep tests inside isolated labs or within a signed scope that lists targets, rates and stop conditions.
What Traces Does Crafted Traffic Leave?
- TCP packets with flag combinations that normal stacks never send.
- Large numbers of SYN packets without the final ACK of a handshake.
- Identical packet sizes and perfectly regular timing.
- Source addresses that are bogons or that never answer return traffic.
- Spikes in half-open connections on the target server.
How Do You Detect hping3-Style Traffic?
IDS engines such as Snort and Suricata include community rules for invalid TCP flag combinations and SYN flood thresholds. Zeek records connection states, so many flows that end in a half-open state stand out. Firewalls with stateful inspection log packets that do not belong to any known session. NetFlow or IPFIX data from routers helps spot volume floods early. CISA's DDoS guidance recommends preparing a response plan and contacts with your provider before an attack.
How Do You Check SYN Flood Protection on Your Linux Server?
This read-only check shows whether SYN cookies are enabled on your own Linux host. The kernel documentation explains that a value of 1 sends cookies when the SYN backlog overflows.
sysctl net.ipv4.tcp_syncookies
sysctl net.ipv4.tcp_max_syn_backlog
How Do You Reduce the Impact of Packet Floods?
| Control | Effect |
|---|---|
| SYN cookies | Server survives backlog exhaustion, as described in RFC 4987 |
| Rate limiting at the edge | Caps new connections per source |
| Stateful firewall | Drops packets outside valid sessions and odd flag sets |
| Anti-spoofing filters | Blocks packets with impossible source addresses |
| Upstream DDoS protection | Absorbs volume before it reaches your link |
To understand the flags involved, read our guide to TCP communication flags, and see our network scanning tool comparison. Safe lab practice is part of our network security training.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.