What Is a VPN Tunnel and How Does VPN Tunnelling Work?
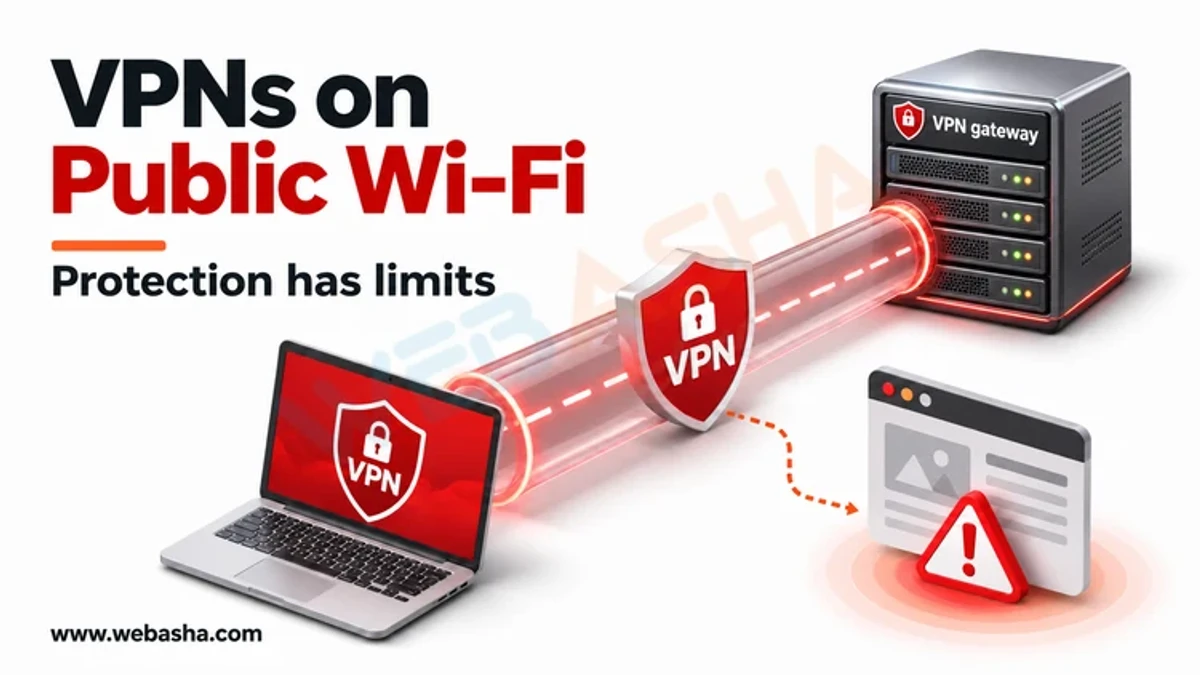
A VPN tunnel is an encrypted connection that carries network traffic between two points over an untrusted network such as the internet. Tunnelling works by encapsulating each original packet inside a new packet: the original is encrypted, wrapped with new headers addressed to the VPN endpoint, sent across the internet, then unwrapped and decrypted at the other end.
Topic: Network Security in Cybersecurity & Ethical Hacking · Explainer
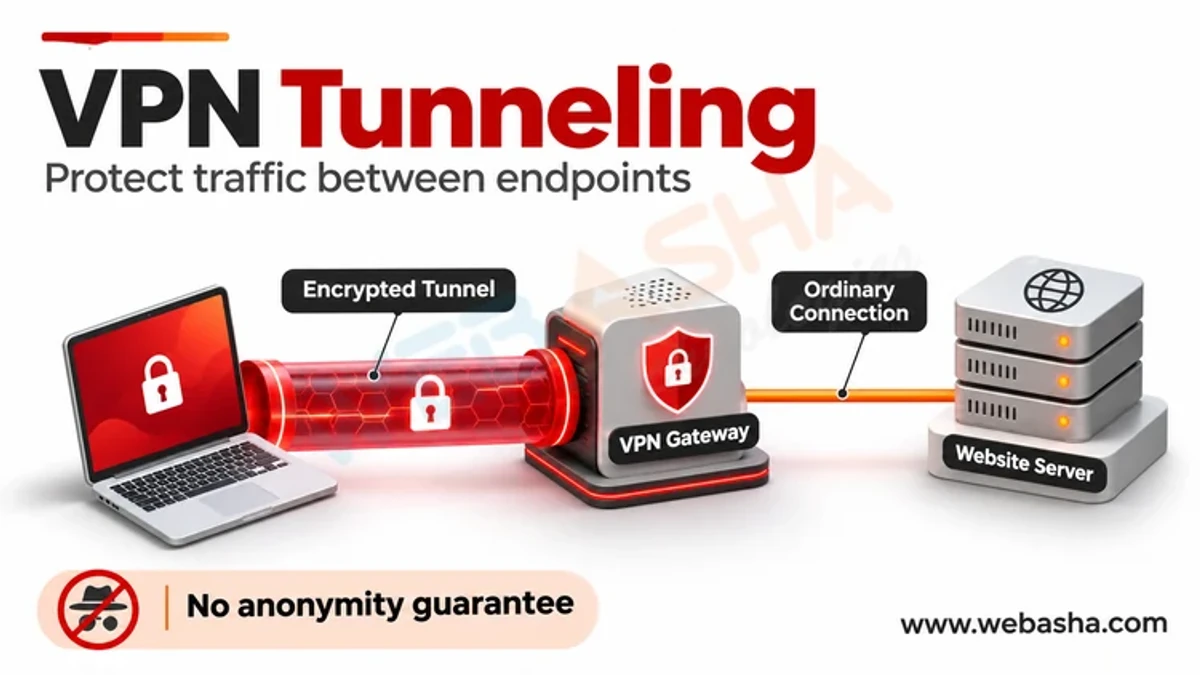
Quick answer: A VPN tunnel is an encrypted connection that carries network traffic between two points over an untrusted network such as the internet. Tunnelling works by encapsulating each original packet inside a new packet: the original is encrypted, wrapped with new headers addressed to the VPN endpoint, sent across the internet, then unwrapped and decrypted at the other end. Its purposes are confidentiality (no one in between can read traffic), integrity (tampering is detected) and access (remote users or offices reach private networks). Common protocols are IPsec with IKEv2, WireGuard and OpenVPN.
Key takeaways
- Tunnelling = encapsulation + encryption + authentication.
- Site-to-site VPNs connect networks; remote access VPNs connect users.
- Split tunnelling sends only corporate traffic through the VPN.
- VPN gateways are prime targets; patch them and use MFA.
- Zero trust access is replacing broad VPN access in many organisations.
Table of Contents
- How Does Tunnelling Work?
- What Types of VPN Tunnels Exist?
- Which Protocols Create VPN Tunnels?
- What Is Split Tunnelling?
- What Does a Simple WireGuard Tunnel Look Like?
- How Do You Secure VPNs?
- References
How Does Tunnelling Work?
- The client and gateway authenticate each other and agree keys (for example with IKEv2 or WireGuard's handshake).
- Each original packet is encrypted and authenticated.
- It is wrapped in an outer packet addressed to the VPN gateway.
- The gateway removes the outer header, verifies and decrypts the packet, and forwards it to the private network.
What Types of VPN Tunnels Exist?
| Type | Connects | Example |
|---|---|---|
| Site-to-site | Two networks | Branch office to head office, data centre to cloud |
| Remote access | A user's device to a network | Employee working from home |
| Cloud VPN | On-premises to cloud VPC | AWS Site-to-Site VPN, Azure VPN Gateway |
Which Protocols Create VPN Tunnels?
| Protocol | Notes |
|---|---|
| IPsec with IKEv2 | Standards-based (RFC 7296), common for site-to-site and mobile; NIST SP 800-77 guidance |
| WireGuard | Modern, small codebase, fixed strong cryptography (whitepaper) |
| OpenVPN | TLS-based, flexible, widely supported |
| SSL/TLS VPNs | Vendor remote access products using TLS |
| PPTP, L2TP without IPsec | Obsolete or insecure; avoid |
What Is Split Tunnelling?
With full tunnelling, all traffic goes through the VPN, giving the organisation full visibility but adding load. Split tunnelling sends only traffic for corporate networks through the VPN and lets internet traffic go directly, improving performance for cloud apps but reducing visibility. Many organisations use split tunnelling with endpoint protection and secure web gateways on devices.
What Does a Simple WireGuard Tunnel Look Like?
# Generate keys on each side
wg genkey | tee privatekey | wg pubkey > publickey

# /etc/wireguard/wg0.conf on the client
[Interface]
PrivateKey = <client-private-key>
Address = 10.8.0.2/24

[Peer]
PublicKey = <server-public-key>
Endpoint = vpn.example.com:51820
AllowedIPs = 10.0.0.0/16          # split tunnel: only the corporate range

# bring it up and check
sudo wg-quick up wg0
sudo wg show
How Do You Secure VPNs?
The NSA and CISA guide Selecting and Hardening Remote Access VPN Solutions recommends:
- Choosing standards-based products from vendors with a record of fast patching.
- Applying updates quickly; VPN flaws are frequently exploited.
- Requiring MFA and strong cryptography; disabling legacy protocols.
- Restricting management interfaces and monitoring logs.
For broader access, consider zero trust network access, which grants per-application access instead of whole-network access. Related: Tor vs VPN for privacy and VPCs. WebAsha offers network security training.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.