How to Become a SOC Analyst: Skills, Tools, Certifications and Path
To become a SOC analyst, build IT foundations first (networking, Windows and Linux, basic scripting), then learn security monitoring: log analysis, SIEM searches, alert triage and incident response. Practise in a home lab with free tools such as Wazuh or Security Onion, map what you see to MITRE ATT&CK, and document your work in a portfolio.
Topic: SOC & Blue Team in Cybersecurity & Ethical Hacking · Certification preparation
Also covers: Cybersecurity Careers & Certifications
Learning path: SOC Analyst, lesson 15 of 16
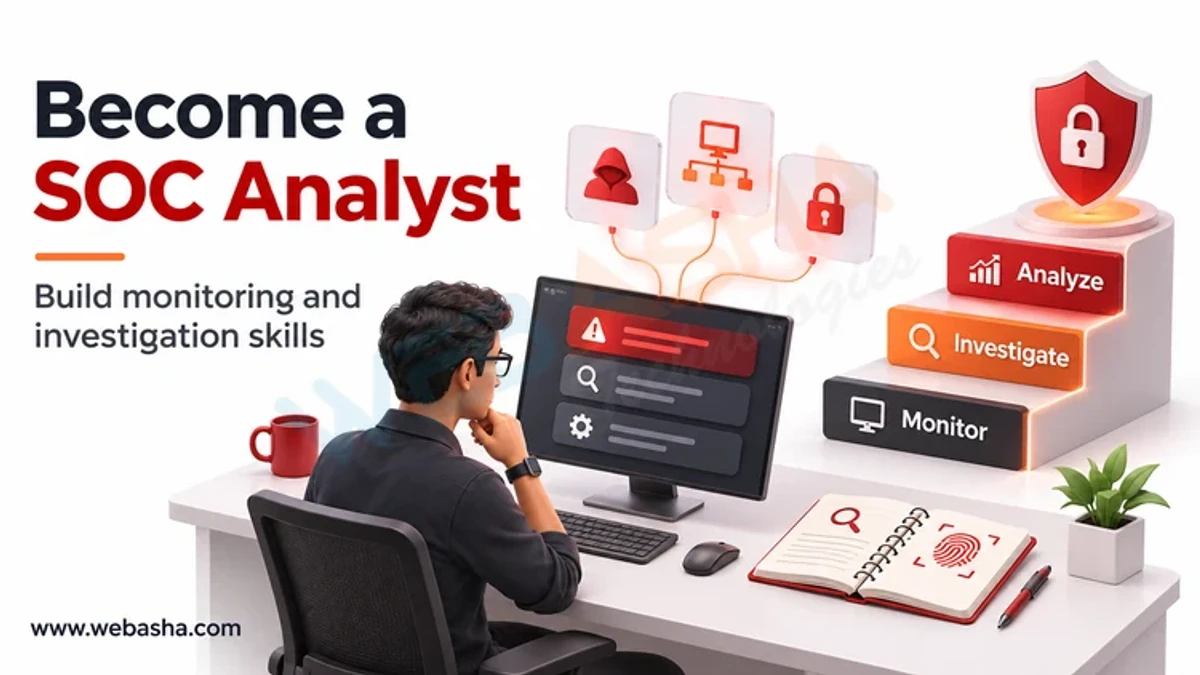
Quick answer: To become a SOC analyst, build IT foundations first (networking, Windows and Linux, basic scripting), then learn security monitoring: log analysis, SIEM searches, alert triage and incident response. Practise in a home lab with free tools such as Wazuh or Security Onion, map what you see to MITRE ATT&CK, and document your work in a portfolio. Entry-level certifications such as CompTIA Security+ and then CySA+ or a vendor SOC certification show employers your knowledge. The NIST NICE Framework describes the work roles and tasks involved, which helps you plan learning. Expect to start in a Tier 1 triage role and grow with experience.
Key takeaways
- A SOC analyst monitors, triages and escalates security alerts.
- Networking and operating system knowledge come before security tools.
- A home lab and written investigations prove practical skill.
- Certifications help, but hands-on evidence matters as much.
- The NICE Framework maps the tasks and skills of SOC roles.
Table of Contents
- What Does a SOC Analyst Do?
- How Does the NICE Framework Describe SOC Work?
- Which Skills Do You Need First?
- Which Tools Should You Learn?
- Which Certifications Help?
- What Does a Step-by-Step Learning Plan Look Like?
- How Do You Show Employers You Are Ready?
- References
What Does a SOC Analyst Do?
A security operations centre watches an organisation's systems around the clock. Analysts review alerts from SIEM, EDR and network tools, decide which are real, gather evidence and escalate or contain incidents following the lifecycle in NIST SP 800-61 Rev. 3. In India, SOC teams also help meet CERT-In's April 2022 directions: report specified incidents within 6 hours and keep logs for 180 days.
| Tier | Typical duties |
|---|---|
| Tier 1 | Monitor queues, triage alerts, close false positives, escalate |
| Tier 2 | Deeper investigation, scoping, containment actions |
| Tier 3 | Threat hunting, detection engineering, complex incidents |
| SOC lead | Shift coordination, metrics, process improvement |
How Does the NICE Framework Describe SOC Work?
The NIST NICE Framework groups work roles under categories such as Protection and Defense. Roles that match SOC work include Defensive Cybersecurity, Incident Response and Threat Analysis. Each lists tasks, knowledge and skills you can use as a checklist. CISA's Cyber Career Pathways Tool shows how these roles connect.
Which Skills Do You Need First?
- Networking: TCP/IP, DNS, HTTP, common ports, reading packet captures.
- Operating systems: Windows event logs, Active Directory basics, Linux logs and permissions.
- Log analysis: what normal looks like, as described in NIST SP 800-92.
- Attacker behaviour: tactics and techniques in MITRE ATT&CK.
- Scripting: basic PowerShell or Python to sort and filter data.
- Communication: clear tickets, timelines and handovers.
Our post on SOC analyst skills and qualifications goes deeper on each.
Which Tools Should You Learn?
| Category | Examples | Why it matters |
|---|---|---|
| SIEM | Splunk, Microsoft Sentinel, Wazuh | Central search and alerting |
| EDR | Microsoft Defender for Endpoint, open source Velociraptor | Endpoint process and file visibility |
| Network | Wireshark, Zeek, Suricata | Traffic evidence |
| Ticketing and SOAR | TheHive, vendor SOAR platforms | Case handling and automation |
Start with how a SIEM works; our SIEM overview is a good primer.
Which Certifications Help?
- Foundation: CompTIA Network+ and Security+, or ISC2 Certified in Cybersecurity.
- Analyst level: CompTIA CySA+, EC-Council CSA, Microsoft SC-200, Splunk certifications.
- Later: GIAC GCIH or GCIA, then specialist tracks.
No certification guarantees a job; pair each one with lab practice.
What Does a Step-by-Step Learning Plan Look Like?
- Learn networking and operating system basics.
- Study security fundamentals and earn a foundation certification.
- Build a lab: a Windows VM, a Linux VM and a free SIEM.
- Generate safe test activity, such as failed logins, and write detections for it.
- Practise on public blue team challenges and write up each investigation.
- Take an analyst-level certification and apply for Tier 1 or NOC roles.
How Do You Show Employers You Are Ready?
Share a portfolio of short investigation reports, detection rules and lab notes. In interviews, explain how you would triage a suspicious login step by step. Structured SOC analyst training with guided labs can shorten the path.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.