Welcome!

Unlock your personalized experience.
Sign Up
Tag

MITRE ATT&CK Framework Articles, Guides & Tutorials

4 posts

How to Become a SOC Analyst: Skills, Tools, Certifications and Path

To become a SOC analyst, build IT foundations first (networking, Windows and Linux, basic scripting), then learn security monitoring: log analysis, SIEM searches, alert triage and incident response. Practise in a home lab with free tools such as Wazuh or Security Onion, map what you see to MITRE ATT&CK, and document your work in a portfolio.
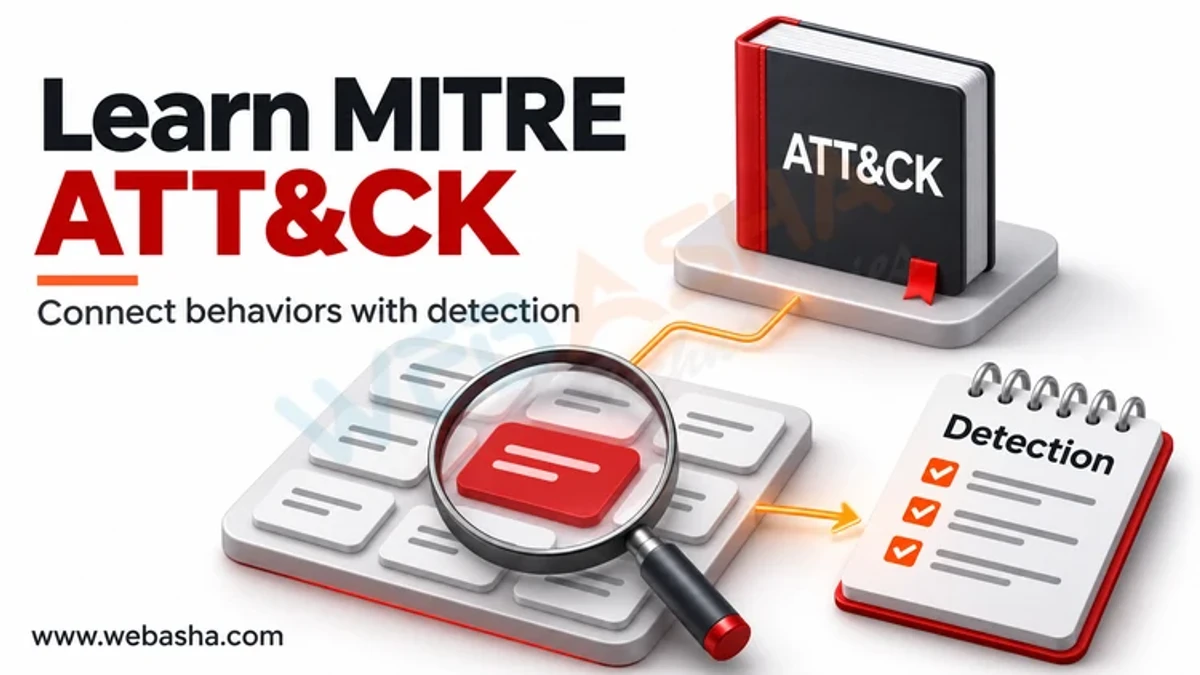
Why Every Ethical Hacker and Defender Should Learn MITRE ATT&CK

MITRE ATT&CK is a free, public knowledge base of the tactics and techniques that real attackers use, built from observed incidents. Ethical hackers should learn it because it gives them a shared language for planning authorised tests and writing reports that defenders can act on. Defenders should learn it because it shows which attacker behaviours their logs and tools can actually detect, and where the gaps are.

MITRE ATT&CK Explained: Map Evidence Without Overstating Coverage

MITRE ATT&CK is a knowledge base of observed adversary behaviour. Its Enterprise domain helps teams relate tactics, techniques, sub-techniques and defensive information to the systems they operate. Use it to organise a question and its evidence, rather than treat a coloured matrix as proof of protection. Record the catalogue version, relevant object and mapping rationale.

MITRE ATT&CK: Turn Coverage Claims into Checkable Evidence

MITRE ATT&CK describes adversary behaviour and related defensive knowledge. It does not scan a network or prove that a mapped technique is detected. To use it practically, identify relevant behaviour, required telemetry, an implemented analytic and evidence from an appropriate review. Keep the platform, asset population and test conditions with any coverage claim.