What Are Red and Blue Teams in Cybersecurity? A Beginner Guide
A red team is an authorised group that emulates real attackers to test an organisation's defences, people and processes. A blue team is the group that defends the organisation by monitoring, detecting, responding to and recovering from attacks, whether real or simulated. When the two work together openly to test and improve detections, the practice is called purple teaming.
Topic: SOC & Blue Team in Cybersecurity & Ethical Hacking · Explainer
Also covers: Penetration Testing
Learning path: SOC Analyst, lesson 2 of 16
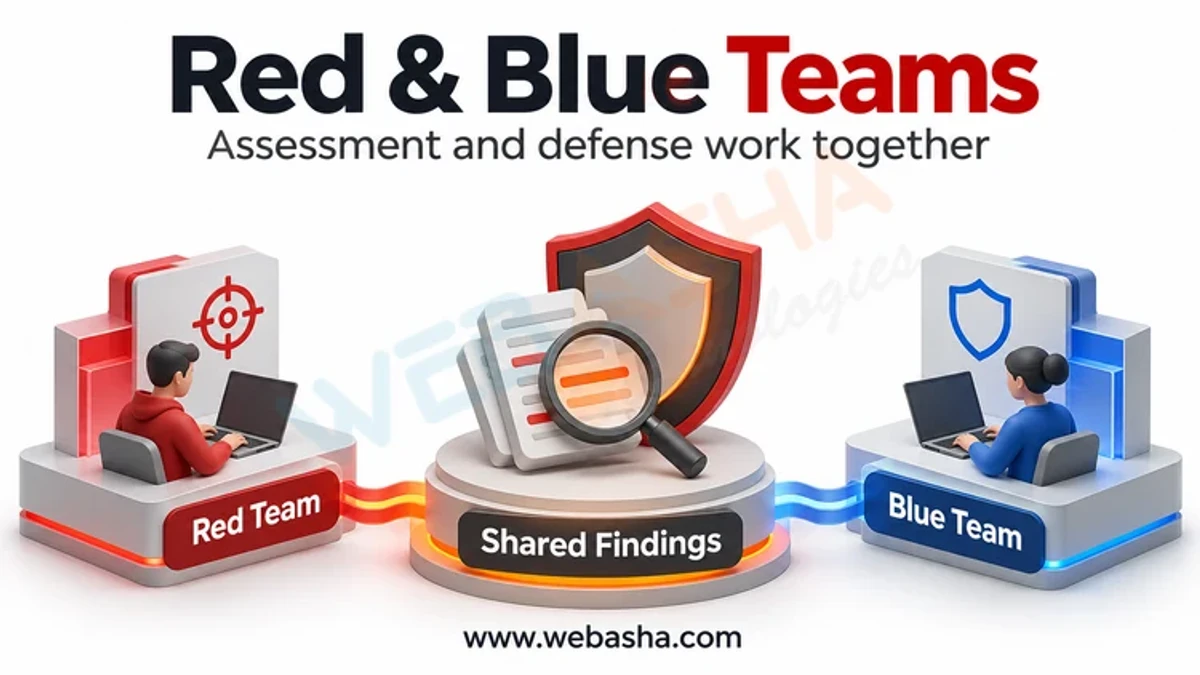
Quick answer: A red team is an authorised group that emulates real attackers to test an organisation's defences, people and processes. A blue team is the group that defends the organisation by monitoring, detecting, responding to and recovering from attacks, whether real or simulated. When the two work together openly to test and improve detections, the practice is called purple teaming. A white team often sets rules and referees exercises. Together they turn theory into measured improvement, using shared frameworks such as MITRE ATT&CK for attacker techniques and MITRE D3FEND for defensive countermeasures.
Key takeaways
- Red teams emulate adversaries; blue teams defend and respond.
- Purple teaming is collaboration between the two, not a separate department.
- All red team activity needs written authorisation and agreed rules.
- Shared frameworks make results measurable and comparable.
- Both paths need strong IT and networking foundations.
Table of Contents
- What Are Red and Blue Teams?
- How Do Red and Blue Teams Differ?
- What Is Purple Teaming?
- How Does a Red and Blue Team Exercise Run?
- Which Frameworks Do Both Teams Use?
- Why Do Organisations Need Both?
- How Can Beginners Choose a Side?
- References
What Are Red and Blue Teams?
NIST defines a red team as a group authorised and organised to emulate a potential adversary's attack or exploitation capabilities against an enterprise's security posture. It defines a blue team as the group responsible for defending an enterprise's use of information systems by maintaining its security posture against a group of mock attackers, and more generally against real threats. NIST SP 800-53 Rev. 5 lists red team exercises as an enhancement to control CA-8.
How Do Red and Blue Teams Differ?
| Aspect | Red team | Blue team |
|---|---|---|
| Goal | Test defences by emulating attackers | Prevent, detect and respond to attacks |
| Typical work | Objective based exercises, social engineering tests, attack path analysis | Monitoring, alert triage, threat hunting, incident response, hardening |
| Common tools | Authorised testing frameworks and lab tooling | SIEM, EDR, network monitoring, ticketing |
| Output | Report of attack paths and detection gaps | Detections, playbooks, incident reports |
| Time frame | Periodic engagements | Continuous, every day |
What Is Purple Teaming?
Purple teaming is a working style in which red and blue teams share plans and results openly, often in the same session. The red team runs a technique, the blue team checks whether it was logged and alerted, and both adjust until detection works. It speeds up learning compared with a covert exercise followed by a report weeks later. See what red and blue teams learn from each other for the lessons this produces.
How Does a Red and Blue Team Exercise Run?
- Plan: leadership and a white team set objectives, scope and rules of engagement, with written authorisation.
- Execute: the red team emulates a chosen threat while the blue team defends as normal.
- Deconflict: a trusted contact confirms whether alerts are part of the exercise.
- Debrief: both teams compare timelines of actions and detections.
- Improve: fixes are assigned and techniques retested.
In India, deconfliction also prevents a false report to CERT-In, since the CERT-In Directions require many incidents to be reported within six hours. Incident handling steps follow guidance such as NIST SP 800-61 Rev. 3.
Which Frameworks Do Both Teams Use?
| Framework | Use |
|---|---|
| MITRE ATT&CK | Catalogue of attacker tactics and techniques |
| MITRE D3FEND | Catalogue of defensive techniques mapped to attacks |
| NIST CSF 2.0 | Outcomes across Govern, Identify, Protect, Detect, Respond, Recover |
| NIST SP 800-61 Rev. 3 | Incident response recommendations |
Why Do Organisations Need Both?
Without a red team, defenders rarely see how a real attack would unfold across their environment. Without a strong blue team, red team findings have nobody to fix them and nothing to measure against. Smaller organisations often hire external red teams periodically while keeping an internal or managed blue team for daily monitoring.
How Can Beginners Choose a Side?
If you enjoy investigation and patterns, start with blue team roles such as SOC analyst. If you enjoy puzzles and thinking like an attacker, aim for penetration testing and later red teaming. Both need networking, operating systems and scripting. Compare paths in red team vs blue team career paths. Practise offensive skills only in labs you own or with written permission, as required by Sections 43 and 66 of the India IT Act 2000. WebAsha offers red team and SOC training.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.