
Welcome!

Unlock your personalized experience.
Sign Up
Tag

Tag: blue team monitoring

2 posts

What Red and Blue Teams Learn From Each Other: Practical Lessons

Red and blue teams learn the most when they review an exercise together. Blue teams learn where their logging and detection are blind, how real attack chains look in their own data, and how quickly they can contain an intrusion. Red teams learn which techniques defenders actually catch, how their activity appears in logs, and how to write findings that lead to fixes.

What Are Red and Blue Teams in Cybersecurity? A Beginner Guide

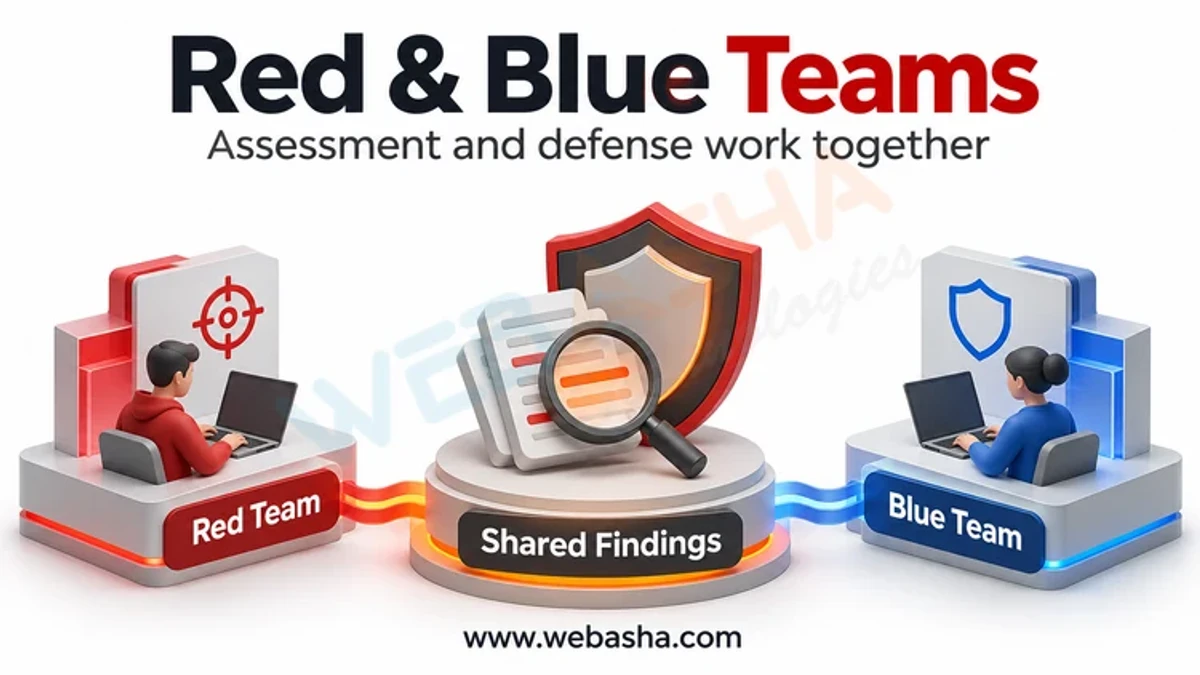
A red team is an authorised group that emulates real attackers to test an organisation's defences, people and processes. A blue team is the group that defends the organisation by monitoring, detecting, responding to and recovering from attacks, whether real or simulated. When the two work together openly to test and improve detections, the practice is called purple teaming.








