Modern Authentication Methods in Cybersecurity Explained
Modern authentication moves beyond passwords alone. The strongest widely available methods are passkeys and FIDO2 security keys, and certificate-based or smart card authentication, which resist phishing. Next come push notifications with number matching and authenticator app codes (TOTP), then SMS codes, which are weakest.
Topic: Active Directory & Identity Security in Cybersecurity & Ethical Hacking · Explainer
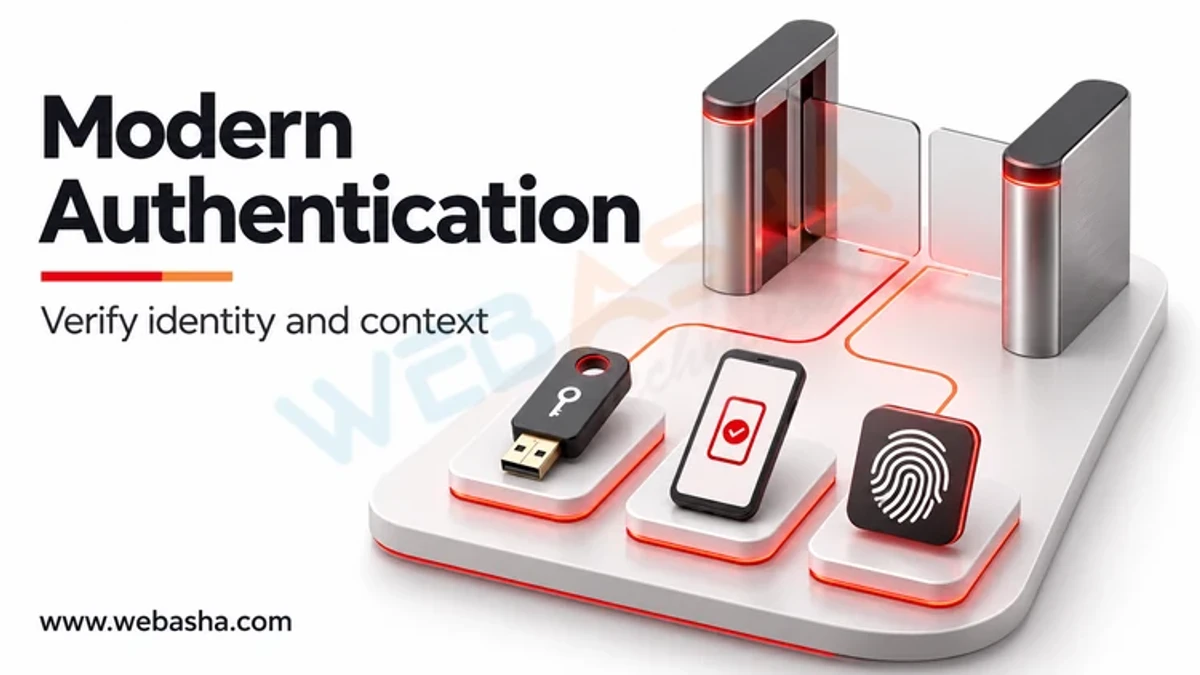
Quick answer: Modern authentication moves beyond passwords alone. The strongest widely available methods are passkeys and FIDO2 security keys, and certificate-based or smart card authentication, which resist phishing. Next come push notifications with number matching and authenticator app codes (TOTP), then SMS codes, which are weakest. These factors are usually combined with single sign-on through standards such as OpenID Connect and SAML, and with conditional access that checks device health and risk. Where passwords remain, NIST now recommends long passphrases, checks against breached passwords and no forced periodic changes.
Key takeaways
- Phishing-resistant MFA (FIDO2, PKI) is the target for most organisations.
- SMS codes are better than nothing but vulnerable to SIM swap and phishing.
- SSO reduces password sprawl and centralises policy.
- Conditional access adds device and risk checks to every sign-in.
- NIST password guidance favours length and breach checks over complexity rules.
Table of Contents
- What Are Authentication Factors?
- How Do Modern Methods Compare?
- How Do SSO and Federation Work?
- What Is Risk-Based and Conditional Access?
- What Are Current Password Rules?
- How Should an Organisation Roll Out Modern Authentication?
- Which Attacks Target Authentication Today?
- References
What Are Authentication Factors?
| Factor | Examples |
|---|---|
| Something you know | Password, PIN |
| Something you have | Phone, security key, smart card |
| Something you are | Fingerprint, face (used locally to unlock a key) |
Multi-factor authentication combines two or more different factors. NIST SP 800-63B Rev. 4 defines assurance levels for these combinations.
How Do Modern Methods Compare?
| Method | Phishing resistant | Notes |
|---|---|---|
| Passkeys / FIDO2 security keys (WebAuthn) | Yes | Bound to the real website domain |
| Certificate-based / smart card | Yes | Common in government and enterprises |
| Push with number matching | Partly | Stops blind approvals and MFA fatigue |
| Authenticator app codes (TOTP) | No | Codes can be phished and relayed |
| SMS or voice OTP | No | SIM swap and interception risks |
CISA's phishing-resistant MFA fact sheet uses the same ordering. See our guide to passkeys for details.
How Do SSO and Federation Work?
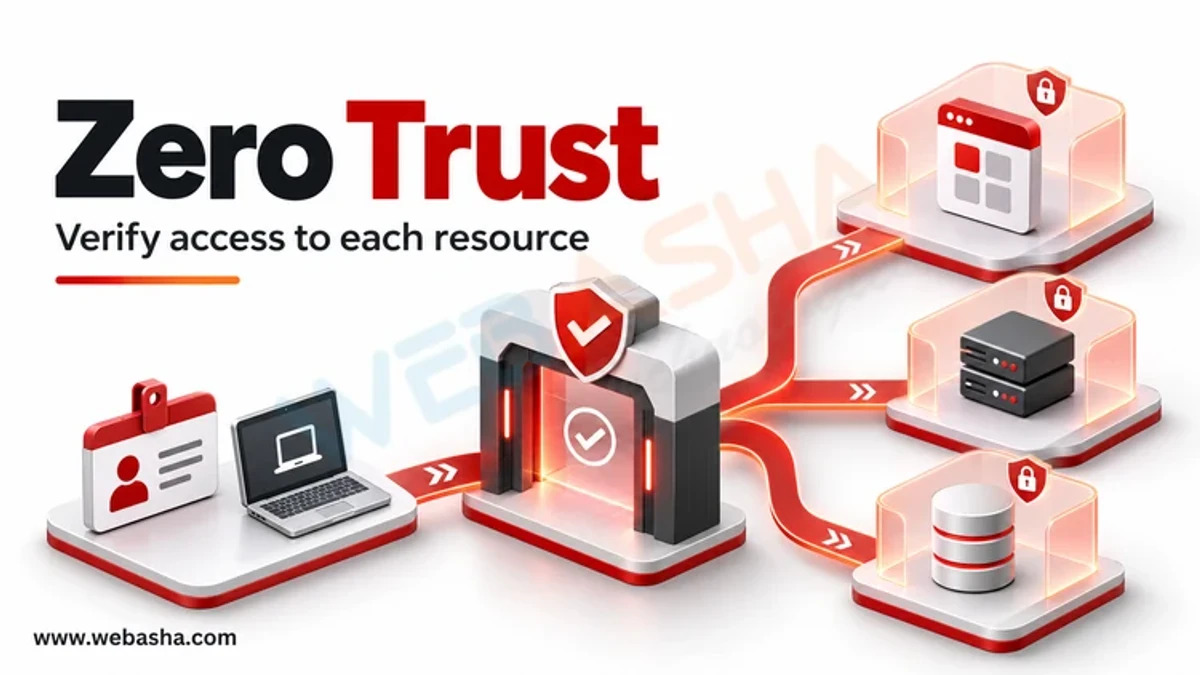
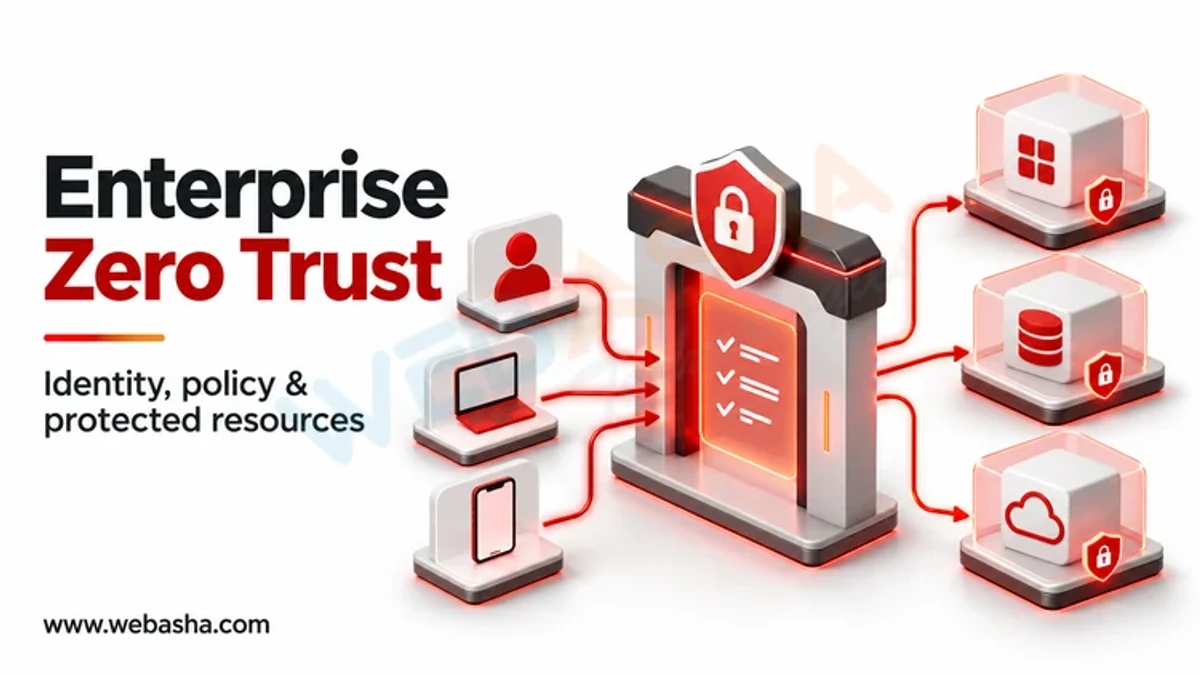
Single sign-on lets users authenticate once at an identity provider, which then vouches for them to applications using OpenID Connect tokens or SAML assertions. Applications never see the password, and MFA and policy are enforced in one place. See what happens in an SSO login.
What Is Risk-Based and Conditional Access?
Conditional access evaluates each sign-in: is the device managed and compliant, is the location unusual, is the user's risk elevated? It then allows, blocks or asks for stronger authentication. Microsoft documents supported authentication methods in Entra ID, and similar features exist in Okta, Google and other identity providers.
What Are Current Password Rules?
- Allow long passwords and passphrases; NIST requires support for at least 64 characters.
- Check new passwords against lists of breached and common passwords.
- Do not force periodic changes; change only on evidence of compromise.
- Do not impose arbitrary composition rules.
- Allow password managers and paste.
How Should an Organisation Roll Out Modern Authentication?
- Consolidate applications behind one identity provider with SSO.
- Enforce MFA for all users, starting with administrators and remote access.
- Enable number matching for push; disable SMS where possible.
- Issue passkeys or security keys to admins and high-risk staff, then everyone.
- Add conditional access based on device compliance.
- Strengthen recovery: help desk identity checks and backup methods.
WebAsha offers identity and access management training.
Which Attacks Target Authentication Today?
| Attack | How it works | Defence |
|---|---|---|
| Password spraying | Common passwords tried across many accounts | MFA, breached password checks, lockout policies |
| Adversary-in-the-middle phishing | Proxy site relays login and steals session cookies | Phishing-resistant MFA (FIDO2) |
| MFA fatigue | Repeated push prompts until the user approves | Number matching, rate limits |
| SIM swap | Attacker takes over phone number for SMS codes | Avoid SMS MFA |
| Help desk social engineering | Caller convinces support to reset MFA | Strong identity verification for resets |
MITRE ATT&CK documents these as password spraying (T1110.003) and MFA request generation (T1621).
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.