What Is Zero Trust Network Architecture and Why Does It Matter?
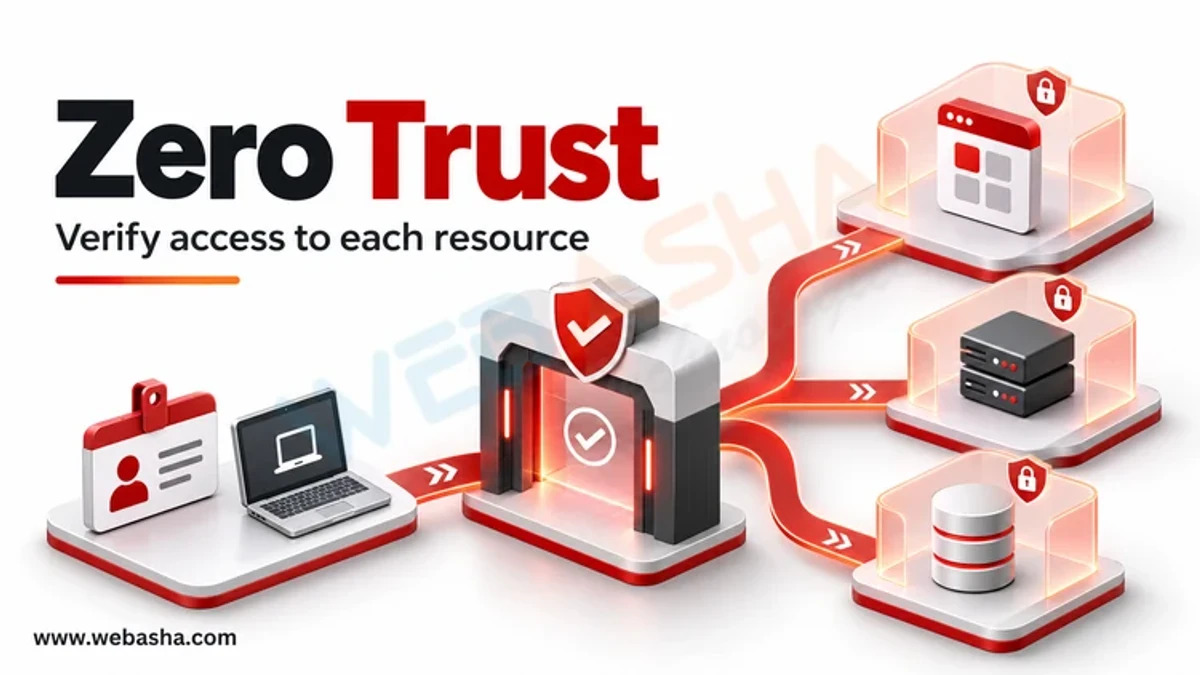
Zero trust network architecture is a security model that removes automatic trust based on network location. Instead of trusting anything inside the corporate network, every request to a resource is checked for who the user is, what device they use, whether that device is healthy, and whether the access fits policy, and access is granted only to that specific resource for that session.
Topic: Active Directory & Identity Security in Cybersecurity & Ethical Hacking · Explainer
Also covers: Cloud & Container Security, Networking, Cybersecurity Foundations
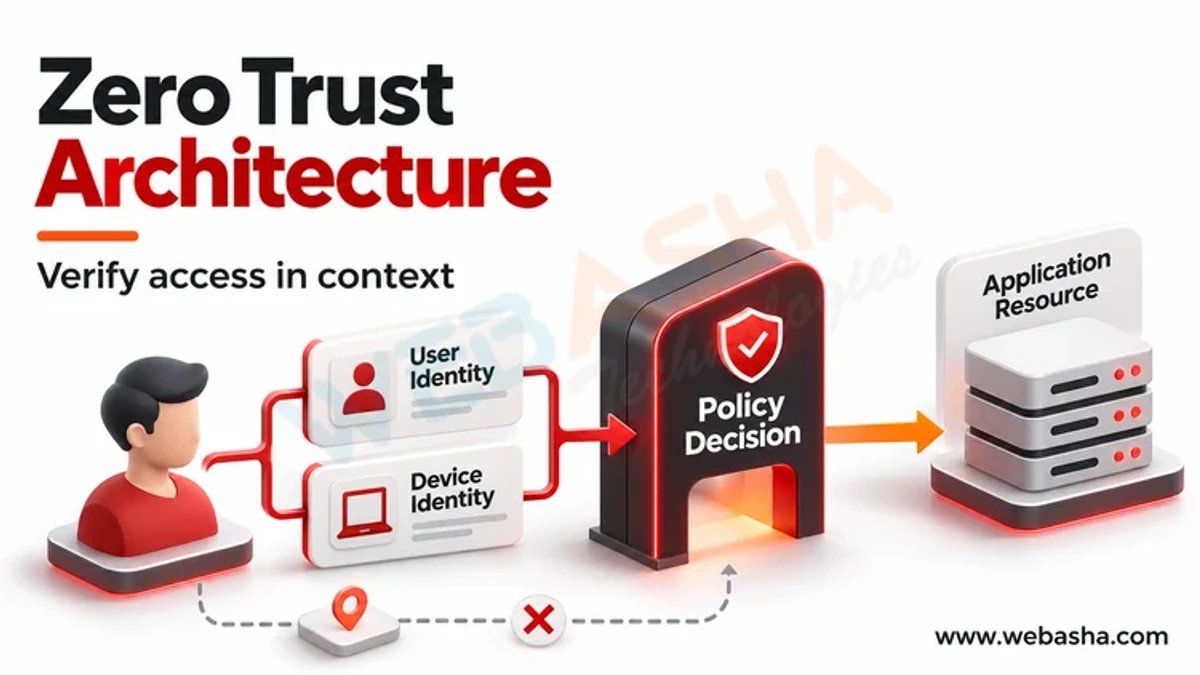
Quick answer: Zero trust network architecture is a security model that removes automatic trust based on network location. Instead of trusting anything inside the corporate network, every request to a resource is checked for who the user is, what device they use, whether that device is healthy, and whether the access fits policy, and access is granted only to that specific resource for that session. NIST SP 800-207 defines the model, and CISA's Zero Trust Maturity Model breaks it into identity, devices, networks, applications and data. It matters because users, apps and data now live outside the old perimeter, and attackers who get inside a trusted network can otherwise move freely.
Key takeaways
- Zero trust means "never trust by location, always verify each request".
- It is an architecture and a journey, not a single product.
- Strong identity, device health and least-privilege access are the foundations.
- Micro-segmentation limits lateral movement if something is compromised.
- CISA's maturity model helps plan progress in stages.
Table of Contents
- What Are the Core Principles of Zero Trust?
- How Does It Differ From Perimeter Security?
- What Are the Components of a Zero Trust Architecture?
- What Are CISA's Five Pillars?
- How Do Organisations Implement Zero Trust?
- What Are Common Misconceptions?
- References
What Are the Core Principles of Zero Trust?
NIST SP 800-207 sets out tenets including:
- All data sources and computing services are resources.
- All communication is secured regardless of network location.
- Access to each resource is granted per session.
- Access is decided by dynamic policy, including user identity, device state and behaviour.
- The organisation monitors the security posture of all assets.
- Authentication and authorisation are strictly enforced before access.
- The organisation collects data to improve its security posture.
How Does It Differ From Perimeter Security?
| Perimeter model | Zero trust | |
|---|---|---|
| Trust basis | Being on the internal network | Verified identity, device and context |
| Remote access | VPN onto the whole network | Access to specific applications only |
| Internal traffic | Mostly allowed | Segmented and authorised |
| After a compromise | Attacker moves laterally | Blast radius limited |
What Are the Components of a Zero Trust Architecture?
| Component (NIST) | Role | Example technology |
|---|---|---|
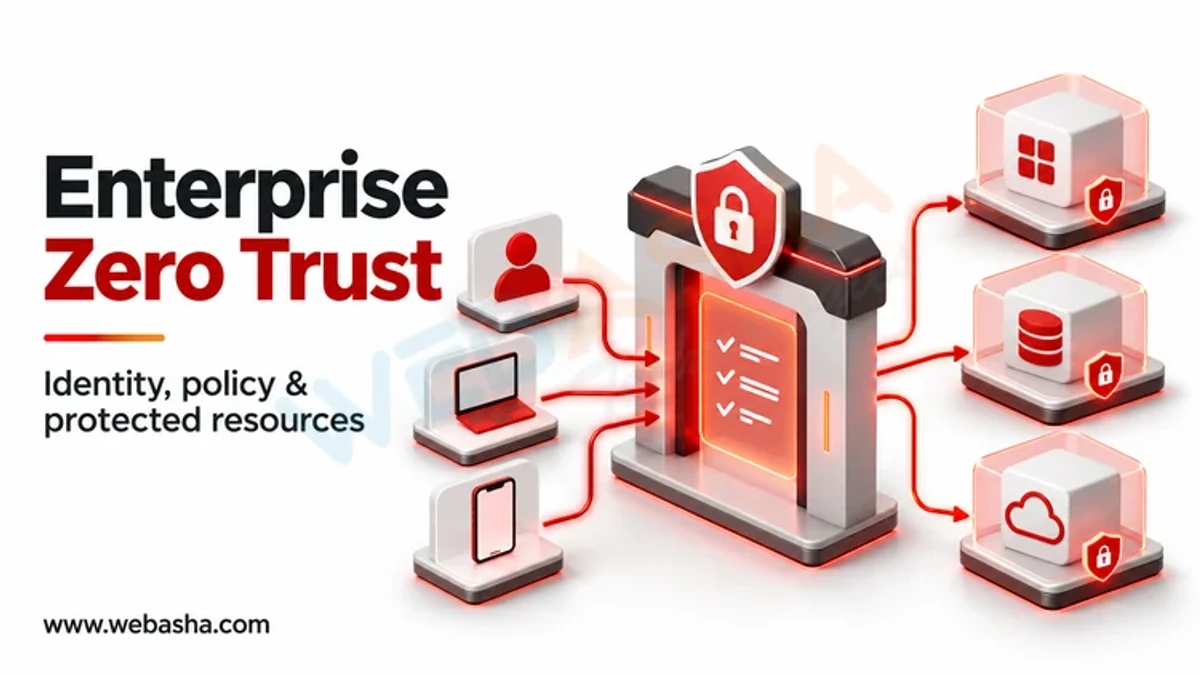
| Policy engine | Decides whether to allow access | Identity provider with conditional access |
| Policy administrator | Sets up or tears down the session | Access broker, ZTNA controller |
| Policy enforcement point | Enforces the decision in the path | Identity-aware proxy, gateway, micro-segmentation agent |
| Signals | Feed decisions | EDR device health, threat intelligence, logs |
A simplified access decision:
IF user authenticated with phishing-resistant MFA
AND device is managed, encrypted and EDR healthy
AND user is in group "Finance"
AND sign-in risk is low
THEN allow access to the finance app only, for this session
ELSE require step-up authentication or deny
What Are CISA's Five Pillars?
The CISA Zero Trust Maturity Model uses five pillars (identity, devices, networks, applications and workloads, data) plus cross-cutting visibility, automation and governance, each with four maturity stages: traditional, initial, advanced and optimal. Organisations rarely move every pillar at the same pace.
How Do Organisations Implement Zero Trust?
- Inventory users, devices, applications and data flows.
- Consolidate identity and enforce phishing-resistant MFA.
- Manage devices and feed health into access decisions.
- Replace broad VPN access with per-application access (ZTNA).
- Segment networks and workloads, starting with crown jewels.
- Centralise logging and automate responses.
NIST SP 1800-35 documents example zero trust builds using commercial products, and the UK NCSC publishes design principles. Google's BeyondCorp and Microsoft's Zero Trust guidance show vendor implementations.
What Are Common Misconceptions?
- "Buy a zero trust product": no single product delivers it.
- "It means trusting no one": it means verifying explicitly, then granting least privilege.
- "VPNs must go immediately": most organisations phase them out gradually.
- "It is only for large enterprises": small firms can start with MFA, device management and app-level access.
Related: zero trust security explained and modern network architecture. WebAsha offers network and cloud security training.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.