Cybersecurity Domains: What Each Area Protects
Cybersecurity domains group related problems, such as protecting identities, applications, infrastructure or organisational information. They overlap: a cloud application can involve access management, secure development, monitoring and governance at the same time. Use domains to understand the controls and evidence needed, then investigate the actual responsibilities of a role.
Topic: Cybersecurity Careers & Certifications in Cybersecurity & Ethical Hacking · Career guidance
Also covers: Cybersecurity Foundations, SOC & Blue Team
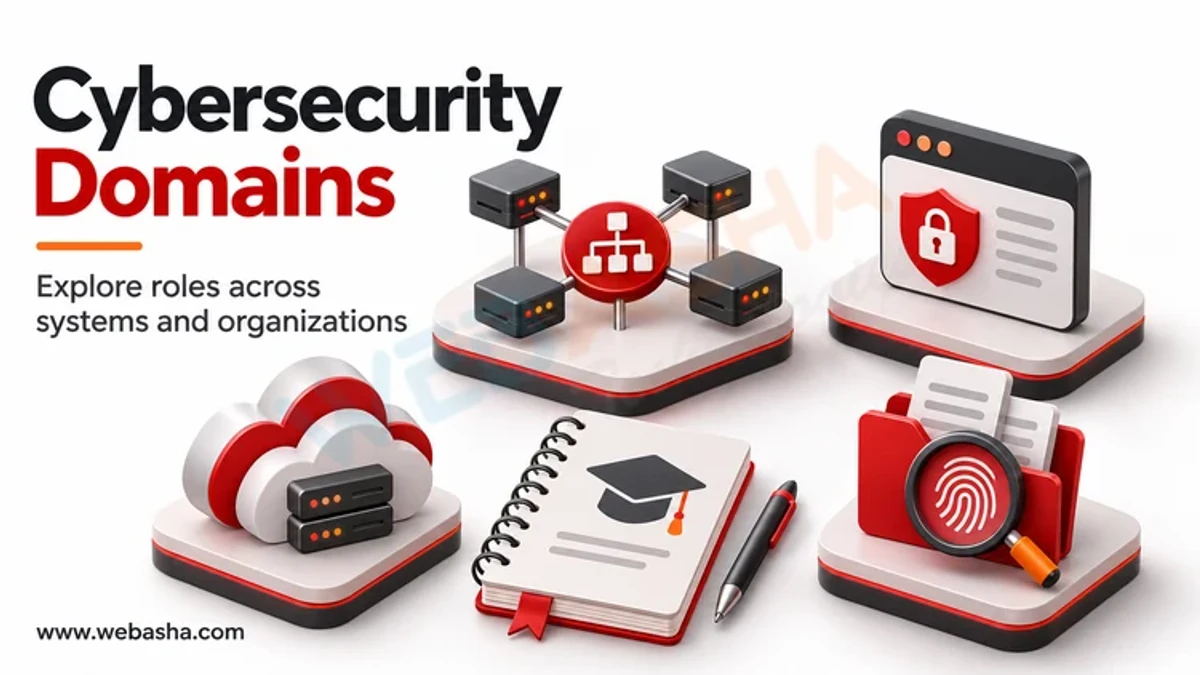
Quick answer: Cybersecurity domains group related problems, such as protecting identities, applications, infrastructure or organisational information. They overlap: a cloud application can involve access management, secure development, monitoring and governance at the same time. Use domains to understand the controls and evidence needed, then investigate the actual responsibilities of a role. There is no single universal domain list or fixed mapping from a domain to a job title. Start with one system and trace how several security areas contribute to its protection.
Key takeaways
- Use domains to understand problems and controls.
- Expect security areas to overlap within the same service.
- Distinguish a technical domain from a job title.
- Look for owners, handoffs and evidence of control operation.
- Choose a learning focus after understanding its dependencies.
Table of Contents
- What is a cybersecurity domain?
- Which technical domains appear in a typical service?
- How does application security connect with development?
- How do monitoring, incident response and threat intelligence connect?
- Which organisational domains support technical controls?
- How can you understand the overlap using one example?
- How should a beginner choose a domain to study?
- References
What is a cybersecurity domain?
A domain is a useful grouping of related security concerns. An organisation might separate application security, identity, cloud security and risk management, while another combines them in a smaller team. The boundaries depend on the environment and how work is organised. A label should help clarify a problem rather than create an assumption that another team owns it.
The NIST Cybersecurity Framework describes organisational cybersecurity outcomes through a risk-management framework. Its functions are not a universal list of technical specialisms. Keep those two views separate: a domain describes the subject you are working on, while a framework can help organise the outcomes and responsibilities the organisation needs.
Which technical domains appear in a typical service?
| Domain | Main question | Example evidence |
|---|---|---|
| Network and platform security | Which connections and system actions are allowed? | Approved configuration and validation records |
| Identity and access management | Who can do what, and who approves it? | Entitlement review and access lifecycle records |
| Application security | How does software resist misuse? | Design review, test findings and remediation evidence |
| Cloud security | Which party operates each control? | Service-model responsibility matrix and configuration review |
| Security monitoring | What events need investigation? | Alert context, analysis and escalation notes |
The AWS IAM: authentication and authorisation illustrates access control in one cloud platform, and the Microsoft Azure shared responsibility shows why cloud responsibilities vary by service model. Neither reference means that every organisation divides its teams in the same way. Check the actual system and contractual responsibilities before assigning work.
How does application security connect with development?
Application security covers decisions made while software is designed, built, tested and maintained. A penetration test can contribute findings, but it does not cover the whole lifecycle. Developers, testers and security reviewers need a way to communicate assumptions, reproduce relevant results and confirm that a change addresses the underlying issue.
The NIST SP 800-218: Secure Software Development Framework provides practices that can be integrated into software development. The OWASP Web Security Testing Guide gives a web-testing reference. Use each for its purpose: one helps structure secure development work, while the other supports specific assessment questions. A completed external test does not establish that every design, dependency or deployment risk has been addressed.
How do monitoring, incident response and threat intelligence connect?
Monitoring produces signals that may need investigation. Incident response coordinates decisions and actions when an event requires handling under the organisation's process. Threat intelligence can add context about relevant activity, but information about an adversary is not evidence that the same activity occurred in your environment.
The MITRE ATT&CK knowledge base can help describe observed behaviours during analysis. Keep the observation, hypothesis and action distinguishable. For a fictional failed-login sequence, identify what is known and which additional records would help. Avoid turning a technique name into a confirmed attribution or assuming that every analyst has authority to disrupt production services.
Which organisational domains support technical controls?
| Area | Contribution | Common dependency |
|---|---|---|
| Governance and risk | Assign ownership and evaluate decisions | Business context and credible technical evidence |
| Assurance | Check whether claims are supported | Defined criteria and access to records |
| Security learning | Help people follow safe workflows | Working tools, reporting channels and operational review |
| Supplier security | Clarify externally operated responsibilities | Contracts, access and escalation arrangements |
| Information handling | Define appropriate use and protection | Data ownership, classification and applicable obligations |
The NIST SP 800-50 Rev. 1: cybersecurity learning programs describes learning-program planning and evaluation. It illustrates how organisational work depends on technical reality. A lesson about reporting an incident needs a functioning channel, just as a policy about access review needs an owner who can obtain and evaluate the relevant records.
How can you understand the overlap using one example?
Consider a fictional customer portal. Identity work defines account permissions; application security examines access checks; cloud security clarifies platform and customer responsibilities; operations reviews suspicious events; governance assigns owners and escalation authority. Each view addresses a different question about the same service. The example describes dependencies rather than a claim about an assessed business.
Draw the service, list the decisions and assign an owner to each. Check where evidence must pass between teams, such as a finding moving from a tester to a developer and then to a reviewer. Missing handoffs can leave a documented problem unresolved even when every team believes its own task is complete.
How should a beginner choose a domain to study?
Choose a question that interests you and identify its prerequisites. Web assessment depends on web behaviour; access review depends on understanding identity and permissions; event analysis depends on system and network context. Complete a small relevant exercise and ask for feedback before committing to a broad specialisation label.
The NIST NICE Framework: tasks, knowledge and skills helps connect work with tasks and skills, while Microsoft Learn: cybersecurity concepts offers introductory concepts. Keep your first learning plan narrow enough to evaluate. Domain familiarity grows through related tasks and feedback, and neither a framework diagram nor a course title by itself establishes competence or access to a particular job.
Related reading: compare job responsibilities; choose a learning direction; compare security and development work.
If you want instructor feedback, ask WebAsha for a syllabus, supervised lab arrangements and written access terms before enrolling.
References
- NIST Cybersecurity Framework
- AWS IAM: authentication and authorisation
- Microsoft Azure shared responsibility
- NIST SP 800-218: Secure Software Development Framework
- OWASP Web Security Testing Guide
- MITRE ATT&CK knowledge base
- NIST SP 800-50 Rev. 1: cybersecurity learning programs
- NIST NICE Framework: tasks, knowledge and skills
- Microsoft Learn: cybersecurity concepts
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.