
Welcome!

Unlock your personalized experience.
Sign Up
Tag

Secure AI prompts Articles, Guides & Tutorials

2 posts

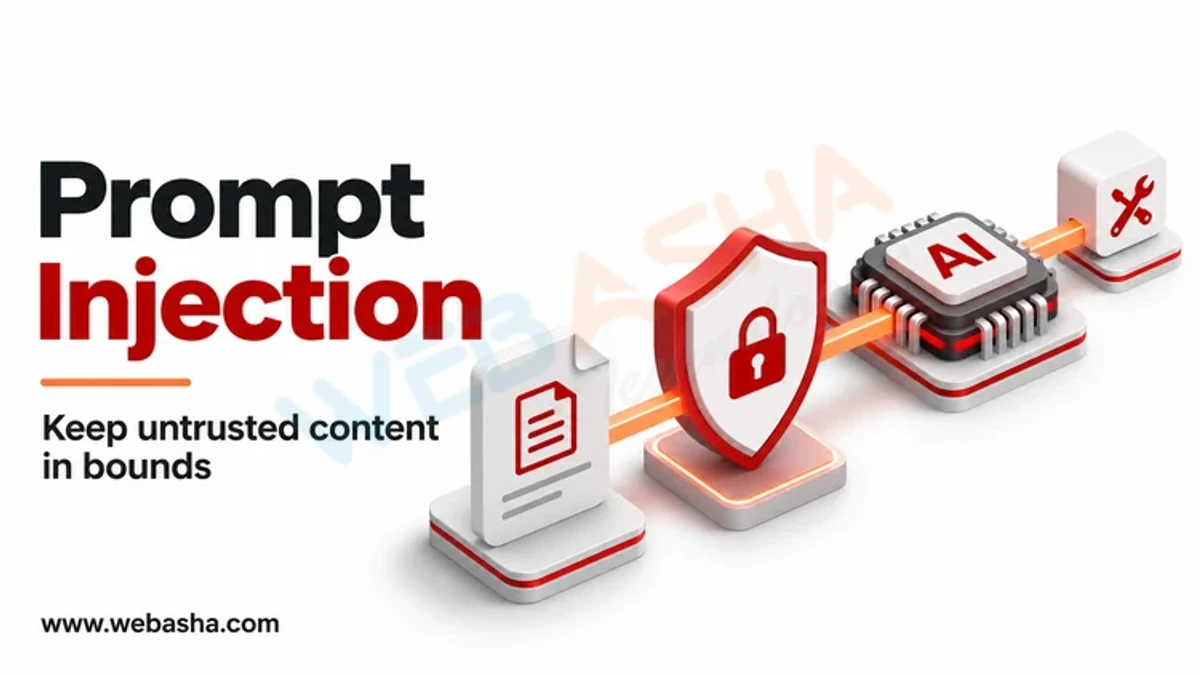
Prompt Injection Attacks in AI: How They Work and How to Reduce Them

Prompt injection is an attack where text given to a large language model (LLM) contains instructions that override what the developer intended. Direct injection comes from the user typing it; indirect injection hides it in content the model reads, such as a web page, email or document. The risk grows when the model can call tools or see private data.
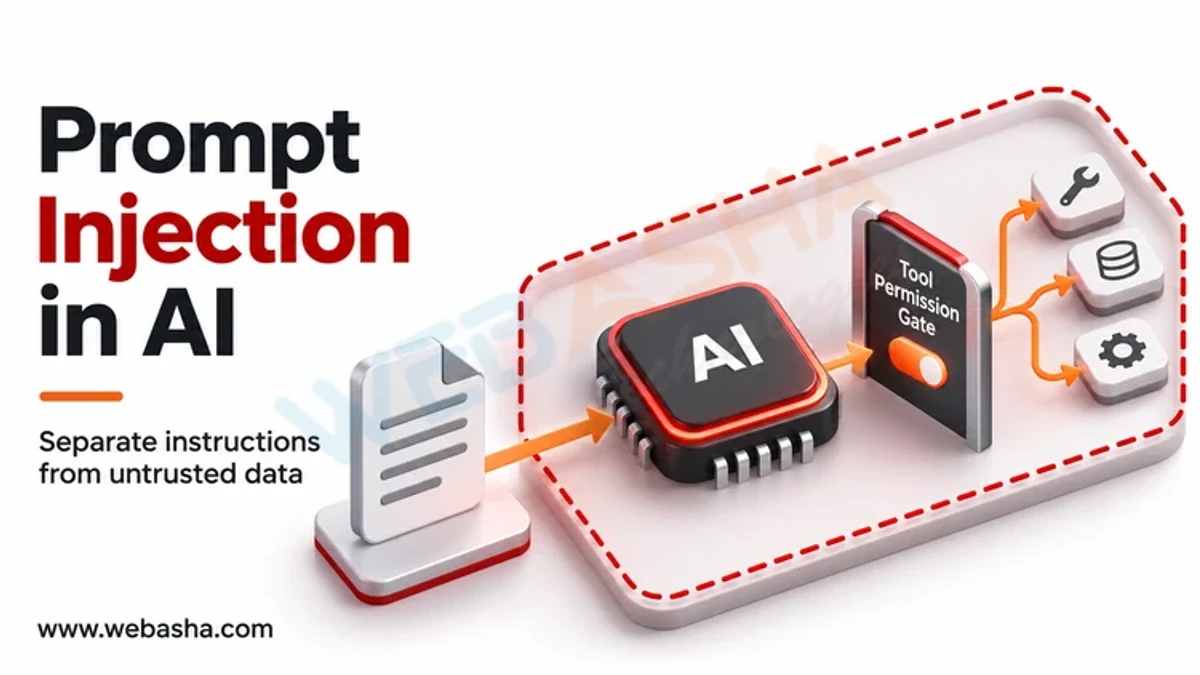

Prompt Injection in Generative AI: How It Works and How to Defend

Prompt injection is an attack in which text supplied to a large language model (LLM) makes it ignore its intended instructions and follow the attacker's instead. In direct injection, a user types the malicious instructions. In indirect injection, the instructions are hidden in content the AI reads, such as a web page, email, document or code comment, so the user may never see them.








