Linux File System Hierarchy Explained: FHS 3.0 and the /usr Merge
Linux arranges everything in one tree that starts at the root directory, /. The Filesystem Hierarchy Standard (FHS) 3.0, published by the Linux Foundation, defines what goes where: /etc holds system configuration, /home holds user files, /var holds changing data such as logs, /usr holds installed programs and libraries, /tmp holds temporary files, and /proc and /sys expose kernel information.
Topic: Linux Administration in IT Infrastructure · Explainer
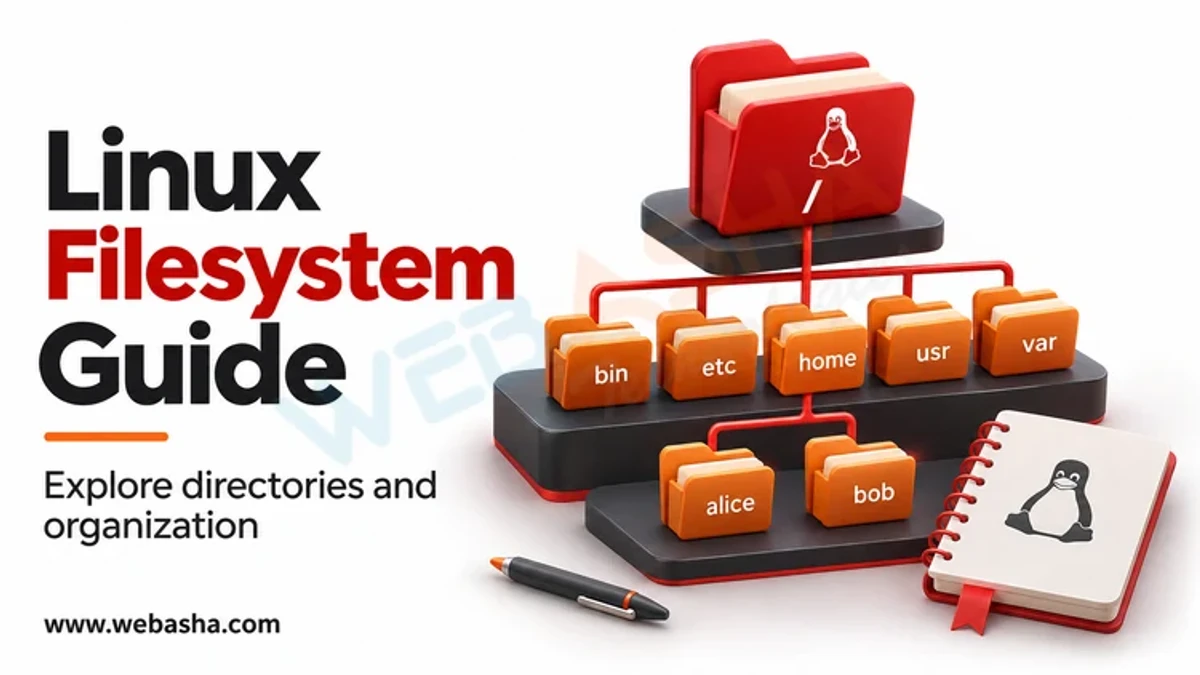
Quick answer: Linux arranges everything in one tree that starts at the root directory, /. The Filesystem Hierarchy Standard (FHS) 3.0, published by the Linux Foundation, defines what goes where: /etc holds system configuration, /home holds user files, /var holds changing data such as logs, /usr holds installed programs and libraries, /tmp holds temporary files, and /proc and /sys expose kernel information. Most current distributions have also merged /bin, /sbin and /lib into /usr, keeping the old names as symbolic links. Knowing the layout helps you administer systems, troubleshoot faster and know where to look during a security investigation.
Key takeaways
- There are no drive letters; disks are mounted somewhere in the single tree.
- FHS 3.0 is the reference for directory purposes.
- On merged-/usr systems, /bin points to /usr/bin.
- /etc, /var/log and home directories matter most in investigations.
- Separate mounts with noexec and nosuid options can harden /tmp.
Table of Contents
- How Is the Linux Directory Tree Organised?
- What Does Each Top-Level Directory Contain?
- What Is the /usr Merge?
- What Are /proc, /sys and /dev?
- Which File System Types Are Common?
- Which Directories Matter Most for Security?
- How Do You Explore the Hierarchy Yourself?
- References
How Is the Linux Directory Tree Organised?
Everything, including disks, USB drives and network shares, appears under /. The FHS 3.0 separates files by two ideas: shareable or local, and static or variable. Programs in /usr are static and shareable; logs in /var are variable and local. The hier(7) and file-hierarchy(7) manual pages describe the layout on your own system.
What Does Each Top-Level Directory Contain?
| Directory | Purpose |
|---|---|
| /boot | Kernel, initramfs and boot loader files |
| /etc | System-wide configuration files |
| /home | Users' personal directories |
| /root | Home directory of the root user |
| /usr | Installed programs, libraries and documentation |
| /usr/local | Software installed locally by the administrator |
| /opt | Add-on packages from third parties |
| /var | Variable data: logs, caches, spool, databases |
| /tmp | Temporary files, often cleared at boot |
| /srv | Data served by this system, such as web content |
| /mnt and /media | Temporary and removable mounts |
| /run | Runtime data since boot, such as PID files |
What Is the /usr Merge?
Historically /bin and /sbin held tools needed before /usr was mounted. Modern systems mount /usr early, so the split no longer helps. The freedesktop.org case for the /usr merge explains the reasoning. Fedora 17 made the move, and the Debian 12 release notes state that a merged /usr is now required. Check yours with ls -ld /bin /sbin /lib; on a merged system they are links to usr/bin, usr/sbin and usr/lib.
What Are /proc, /sys and /dev?
These are not stored on disk. /proc shows processes and kernel settings, for example /proc/cpuinfo and /proc/PID/cmdline. /sys exposes devices and drivers. /dev contains device files such as /dev/sda and /dev/null. Reading them is a safe way to learn about a running system.
Which File System Types Are Common?
| Type | Typical use |
|---|---|
| ext4 | Default on Debian and Ubuntu |
| XFS | Default on RHEL |
| Btrfs | Default on Fedora Workstation; snapshots |
| tmpfs | Memory-backed /run and often /tmp |
| vfat | EFI system partition at /boot/efi |
Which Directories Matter Most for Security?
- /etc: passwd, shadow, sudoers, ssh and cron settings; changes here deserve alerts.
- /var/log: authentication and system logs; protect them and ship copies off the host.
- /tmp and /dev/shm: world-writable, so attackers often drop files there. The CIS Benchmarks recommend separate mounts with nodev, nosuid and noexec.
- Home directories: check .ssh/authorized_keys and shell startup files for unexpected entries.
Permissions decide who can use each directory; see our file permissions guide.
How Do You Explore the Hierarchy Yourself?
ls -l /                       # top-level directories
findmnt                       # what is mounted where
df -hT                        # usage and file system types
du -sh /var/log               # size of the log directory
sudo find /etc -mtime -1      # config files changed in the last day
Our FHS overview adds more background. Build these skills with labs in our Linux administration training.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

Vaishnavi is a skilled tech professional at the Ethical Hacking Training Institute in Pune, responsible for managing and optimizing the technical infrastructure that supports advanced cybersecurity education. With deep expertise in network security, backend operations, and system performance, she ensures that practical labs, online modules, and assessments run smoothly and securely. Her behind-the-scenes contributions play a vital role in delivering a seamless and secure learning experience for aspiring ethical hackers.