What Is NAT? Address Translation, PAT and a Worked Example
Network Address Translation changes address information as traffic crosses a translating device. Basic NAT maps addresses; Network Address Port Translation, often called PAT, also uses transport identifiers so multiple internal endpoints can share an outside IPv4 address. Static and dynamic describe how mappings are assigned.
Topic: Networking in IT Infrastructure · Explainer
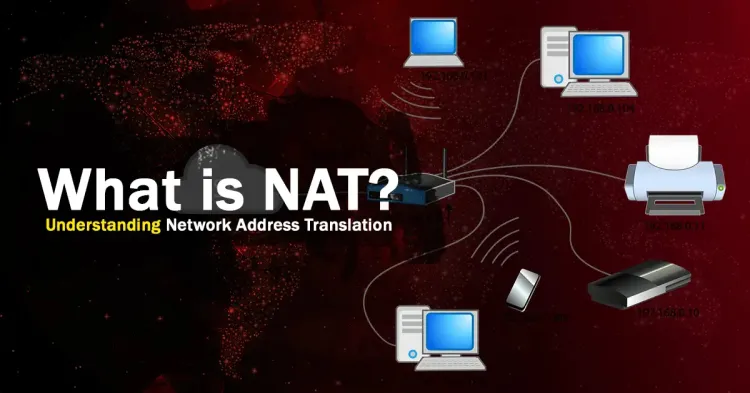
Quick answer: Network Address Translation changes address information as traffic crosses a translating device. Basic NAT maps addresses; Network Address Port Translation, often called PAT, also uses transport identifiers so multiple internal endpoints can share an outside IPv4 address. Static and dynamic describe how mappings are assigned. NAT can support private-address connectivity, but translation does not establish encryption, user identity or an access-control policy. The local example below explains a supplied one-to-one map and its reverse without configuring a router or processing real traffic.
Key takeaways
- Distinguish address-only NAT from address-and-port translation.
- Read both the original and translated endpoint information.
- A static one-to-one map does not itself provide many-to-one sharing.
- Keep routing, filtering and translation as separate checks.
- Record mapping context and time when investigating a connection.
Table of Contents
- What information does NAT change?
- Why are private IPv4 addresses used with NAT?
- How do static NAT, dynamic NAT and PAT differ?
- What does a checked one-to-one mapping demonstrate?
- How does a translator distinguish return traffic?
- Does NAT provide firewall protection or encryption?
- What should you check when NAT communication fails?
- References
What information does NAT change?
RFC 3022 describes traditional NAT and Network Address Port Translation. A source translation can change the source address seen beyond the translator; a destination translation can change where a packet is directed. With address-and-port translation, transport identifiers also participate. The exact operation depends on the configured mode and traffic direction.
Imagine a classroom client with an internal address contacting an external service. The outside service can observe the translated endpoint rather than the original inside address. That does not mean the inside device vanished, became anonymous or acquired permission to use every outside service. The translator’s state, routing and applicable filtering still determine what happens to the traffic.
Why are private IPv4 addresses used with NAT?
RFC 1918 defines the private IPv4 ranges, including 10.0.0.0/8, 172.16.0.0/12 and 192.168.0.0/16. These addresses support private-network use and are not ordinary globally routed assignments. Not every 172.x address is private; the prefix boundary matters. Separate organisations can reuse private addressing, which can create overlap when their networks later connect.
Many-to-one address-and-port translation reduces how many outside addresses a set of internal endpoints needs. Address-only one-to-one translation serves a different mapping arrangement and does not automatically achieve that same reduction. Also distinguish private addresses from documentation values. RFC 5737 reserves the 192.0.2.0/24 block used below for examples; those outside-side values are not real public addresses assigned to this classroom.
How do static NAT, dynamic NAT and PAT differ?
A static mapping is configured to remain associated with a particular inside endpoint. Dynamic address translation allocates from an address pool under its policy. PAT translates addresses and transport identifiers, allowing several endpoints to use one outside address while their flows remain distinguishable.
These descriptions are related dimensions, not a promise that every vendor uses identical commands or allocation rules. Pool size, timeouts, protocol handling and mapping behaviour affect capacity and troubleshooting. A static translation may be part of publishing a service, but it does not by itself create a listener, install the required route or grant access through a firewall. Check those conditions before assuming that a published mapping makes the service reachable.
| Arrangement | Main distinction | Question for the operator |
|---|---|---|
| Static address map | Configured address association | Is the intended mapping present? |
| Dynamic address pool | Allocation from available addresses | What happens when the pool is exhausted? |
| PAT/NAPT | Address plus transport identifier translation | Which mapping identifies this flow? |
What does a checked one-to-one mapping demonstrate?
This Python 3 exercise parses supplied address strings using ipaddress. It requires unique outside addresses, constructs a reverse map and identifies one absent inside mapping. It does not implement a NAT device, alter packet headers, open sockets or inspect a router. The uniqueness check belongs to this declared one-to-one exercise.
from ipaddress import IPv4Address

mapping = {
    IPv4Address("10.0.0.10"): IPv4Address("192.0.2.10"),
    IPv4Address("10.0.0.11"): IPv4Address("192.0.2.11"),
}
if len(set(mapping.values())) != len(mapping):
    raise ValueError("this exercise requires unique outside addresses")
reverse = {outside: inside for inside, outside in mapping.items()}
for supplied in ("10.0.0.10", "10.0.0.11", "10.0.0.12"):
    inside = IPv4Address(supplied)
    outside = mapping.get(inside)
    if outside is None:
        print(f"{inside}: NO MAPPING")
    else:
        print(f"{inside} -> {outside} -> {reverse[outside]}")
print("Distinct outside addresses:", len(reverse))
Expected output:
10.0.0.10 -> 192.0.2.10 -> 10.0.0.10
10.0.0.11 -> 192.0.2.11 -> 10.0.0.11
10.0.0.12: NO MAPPING
Distinct outside addresses: 2
Two inside addresses use two distinct outside addresses here. The third has no supplied mapping; the script does not silently allocate one. A reply-side lookup can recover the corresponding inside value in this small map. A real NAT implementation has additional protocol, lifetime, checksum, routing and policy requirements that this dictionary does not exercise.
How does a translator distinguish return traffic?
For address-and-port translation, record the relevant protocol and original and translated transport endpoints. Two clients using the same outside address need more context than that address alone. A log containing only an outside IP can be insufficient to identify a particular internal connection, especially when mappings are reused over time.
The UDP NAT behavioural requirements distinguish mapping and filtering behaviour. Its scope is unicast UDP, so do not turn every rule there into a universal statement about TCP or every NAT product. Operators should consult the actual device documentation for supported behaviour and lifetimes. Keep observation time and the appropriate mapping records together when comparing evidence from opposite sides of a translator.
Does NAT provide firewall protection or encryption?
Address translation can change what outside observers see, but that transformation is not encryption and is not a complete access policy. Filtering decides which traffic may pass. A device can combine both functions while they remain different questions. An unwanted request through an intentionally published service still needs application and identity controls.
RFC 4864 discusses local-network protection without treating address translation as a prerequisite for every security objective. Choose the control for the requirement: restricting reachability, protecting credentials, encrypting a flow and authorising an operation need their own evidence. Do not conclude that a private address, a NAT table or an absent unsolicited mapping establishes that the endpoint cannot be compromised.
What should you check when NAT communication fails?
Start with the intended service, address family and flow direction. Confirm the supplied inside endpoint and expected outside mapping, then examine routing, filtering, service availability and return-path handling under an authorised plan. Address overlap, exhausted allocation capacity, expired state or applications embedding address information can require different investigations. One failed connection does not identify which condition occurred.
IPv6 and IPv4 interoperability is another distinct requirement. RFC 6146 specifies stateful NAT64 for particular IPv6-to-IPv4 communication; it is not a statement that all IPv6 traffic needs traditional IPv4 NAT. In the classroom, finish by explaining which mapping fact is established and which operational checks remain. Keep the table, test conditions and relevant time together so another administrator can reproduce the reasoning.
| Observed fact | What remains to verify |
|---|---|
| Mapping exists | Required route, filter and service |
| No mapping in supplied table | Whether this mode should allocate one |
| Outside address observed | Protocol, ports, time and mapping context |
| One address family works | The other family’s independent path |
Related reading: Firewall policy and traffic filtering; NAT interview reasoning.
References
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

I am passionate about technology, invention and big challenging tasks on my to- do list. In terms of the work I am doing also at Bunnyshell, I am most passionate about the technologies that we are using., I'm devoted to delivering content that not only informs but also inspires. Whether you need in- depth analysis pieces, educational attendants, or study- provoking opinion pieces, I draft content that resonates with tech suckers and professionals likewise.