What Is a Honeypot in Cybersecurity? Types, Uses and How to Run One
A honeypot is a decoy system, service or file set up to look valuable to an attacker but with no legitimate use, so any interaction with it is suspicious by definition. Security teams use honeypots to detect intruders early, to study how attackers behave, and to collect indicators such as IP addresses, passwords tried and malware dropped.
Topic: Cybersecurity Foundations in Cybersecurity & Ethical Hacking · Explainer
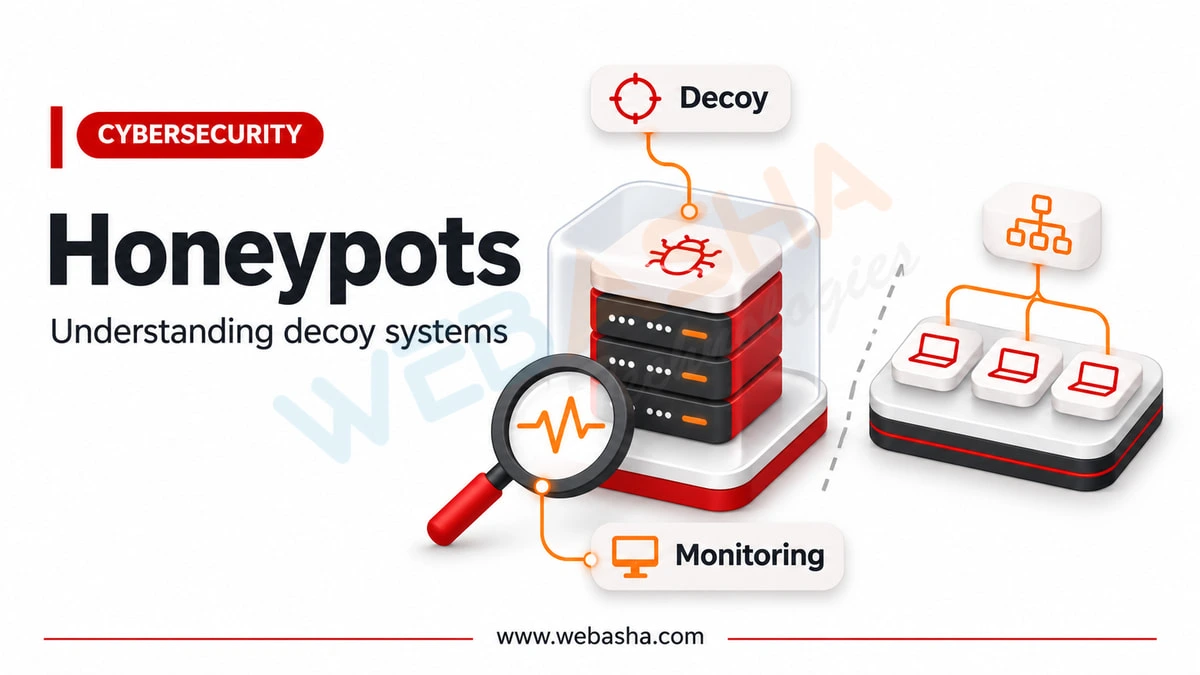
Quick answer: A honeypot is a decoy system, service or file set up to look valuable to an attacker but with no legitimate use, so any interaction with it is suspicious by definition. Security teams use honeypots to detect intruders early, to study how attackers behave, and to collect indicators such as IP addresses, passwords tried and malware dropped. Inside a corporate network, a well-placed honeypot gives some of the highest-confidence alerts you can get, because no normal user should ever touch it.
Key takeaways
- A honeypot has no production purpose, so every connection to it is worth a look.
- Low-interaction honeypots emulate services safely; high-interaction ones are real systems and riskier.
- Internet-facing honeypots study attackers; internal ones detect intruders already inside.
- Isolate honeypots carefully so they cannot become a launch point for real attacks.
- Open-source tools such as Cowrie and OpenCanary make a first honeypot a short exercise.
Table of Contents
- What Is a Honeypot?
- Why Is a Honeypot Alert So Reliable?
- What Are the Types of Honeypot?
- How Do You Run an SSH Honeypot?
- How Do You Use a Honeypot Inside a Network?
- What Can a Honeypot Teach You?
- What Are the Risks?
- What Are Honeytokens and Deception Technology?
- Are Honeypots Legal?
- References
What Is a Honeypot?
It is a trap built from something an attacker wants: an open SSH server, a database, a file share, an industrial controller, or a file named passwords. It records everything that happens to it. Researchers at the Honeynet Project have used honeypots for years to study real attacks, and defenders now use the same idea to detect intrusions.
Why Is a Honeypot Alert So Reliable?
Most detection tools look for bad behaviour among a sea of normal behaviour, which is why they produce false positives. A honeypot flips that. Nothing legitimate uses it, so the baseline is zero. One login attempt on an internal decoy server is unusual enough to investigate. Attackers who have just broken in typically explore the network, a step MITRE ATT&CK calls network service discovery, and that exploration is exactly what trips a well-placed decoy. NIST SP 800-94 describes intrusion detection more broadly; honeypots complement those systems with almost noise-free signals.
What Are the Types of Honeypot?
| Type | What it is | Strength | Risk and effort |
|---|---|---|---|
| Low-interaction | Emulates a service, such as a fake SSH login prompt | Safe, cheap, easy to deploy many | Low; attackers can sometimes spot the emulation |
| Medium-interaction | Emulates a fuller shell and file system | Captures commands and downloaded files | Moderate |
| High-interaction | A real, deliberately exposed system | Shows complete attacker behaviour | High; needs strong isolation and monitoring |
| Research honeypot | Internet-facing, built to study attackers | Intelligence on tools and campaigns | Ongoing analysis effort |
| Production honeypot | Inside the network, built to detect intrusions | High-confidence alerts | Low once placed well |
How Do You Run an SSH Honeypot?
Cowrie is a widely used medium-interaction SSH and Telnet honeypot. It accepts logins, presents a fake shell, and logs every command and download. Its documentation covers full installation; the quickest start uses the official container image on a disposable machine:
# run Cowrie, listening on port 2222
docker run -d --name cowrie -p 2222:2222 cowrie/cowrie

# from another machine, try to log in as an attacker would
ssh -p 2222 root@HONEYPOT_IP

# watch what it records
docker logs -f cowrie
Run it on a cloud virtual machine or lab host that holds nothing of value, never on a machine that also does real work. If you expose port 22 to the internet by redirecting it to 2222, keep your real SSH access on a different port with key-only authentication.
How Do You Use a Honeypot Inside a Network?
Internal decoys catch intruders and malicious insiders. OpenCanary from Thinkst is an open-source daemon that pretends to be services such as SSH, FTP, SMB or a web login, and alerts when anything touches them:
python3 -m venv canary && . canary/bin/activate
pip install opencanary
opencanaryd --copyconfig        # writes a starter config file
# edit the config: enable the services you want and set where alerts go
opencanaryd --start
Placement matters more than the tool. Put decoys where an intruder would look: a server named like a backup or finance host in the server subnet, a fake file share with tempting folder names, a decoy admin login page. Then make sure alerts go somewhere someone reads them.
What Can a Honeypot Teach You?
- Which usernames and passwords attackers try first, a direct argument for strong, unique credentials.
- Which commands they run after login and what malware they try to download.
- Which IP addresses and infrastructure are scanning, useful for blocking and threat intelligence.
- Inside a network: that someone is exploring, and from which host, which is often the first sign of a breach.
What Are the Risks?
- Becoming a launch point. A badly isolated high-interaction honeypot can be used to attack others. Restrict its outbound traffic tightly.
- Detection by attackers. Skilled attackers can recognise emulated services and avoid them or feed them false data.
- Alert fatigue on the internet. Internet-facing honeypots see constant automated scanning; treat them as research, not as incident alerts.
- Data handling. Captured data may include stolen credentials or personal data of third parties; store and handle it carefully.
What Are Honeytokens and Deception Technology?
A honeytoken is a decoy piece of data rather than a system: a fake password in a configuration file, a fake cloud access key, a fake customer record, or a document that reports when it is opened. If that data is ever used, you know it was stolen. Commercial deception platforms extend this across a network with many decoys and central management. Our article on deception technology explains how these platforms work.
Are Honeypots Legal?
Running a honeypot on your own systems is generally lawful, but two cautions apply. Do not use a honeypot to attack back or to access the attacker's systems, which would be unauthorised access under the Information Technology Act, 2000. And treat any personal data the honeypot captures responsibly, in line with your data protection obligations. Take advice before using captured material in legal proceedings.
For related detection controls, see IDS and IPS explained.
Talk to a WebAsha training advisor about SOC and blue team courses, batches and current fees.
References
- The Honeynet Project
- Cowrie SSH and Telnet honeypot
- Cowrie documentation
- OpenCanary, Thinkst
- NIST SP 800-94, Guide to Intrusion Detection and Prevention Systems
- MITRE ATT&CK T1046, Network Service Discovery
Related reading
Frequently Asked Questions
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0

I am passionate about technology, invention and big challenging tasks on my to- do list. In terms of the work I am doing also at Bunnyshell, I am most passionate about the technologies that we are using., I'm devoted to delivering content that not only informs but also inspires. Whether you need in- depth analysis pieces, educational attendants, or study- provoking opinion pieces, I draft content that resonates with tech suckers and professionals likewise.